Anthropic Warns: Self-Replicating AI Worms Could Infiltrate Smart Devices
New research from **Anthropic** suggests that small AI models are rapidly approaching the capability to self-replicate across consumer Internet of Things (IoT) devices. This could lead to the formation of distributed botnets capable of running AI workloads without reliance on traditional data centers, posing a significant challenge for cybersecurity.

**Anthropic** has issued a stark warning regarding the potential for small AI models to soon self-replicate across a wide array of consumer IoT devices. From **Android TV** boxes to smart ovens, these models could form distributed botnets, executing AI tasks independently of centralized data centers.
The company's experiments demonstrated that AI models could identify unfamiliar devices, integrate them into a network, and prepare them to host an AI model. While researchers successfully distributed **Google DeepMind's Gemma4-26B-A4B** model across 15 off-brand **Android TV** boxes, a fully autonomous, self-replicating AI worm running on real IoT hardware was not yet achieved.
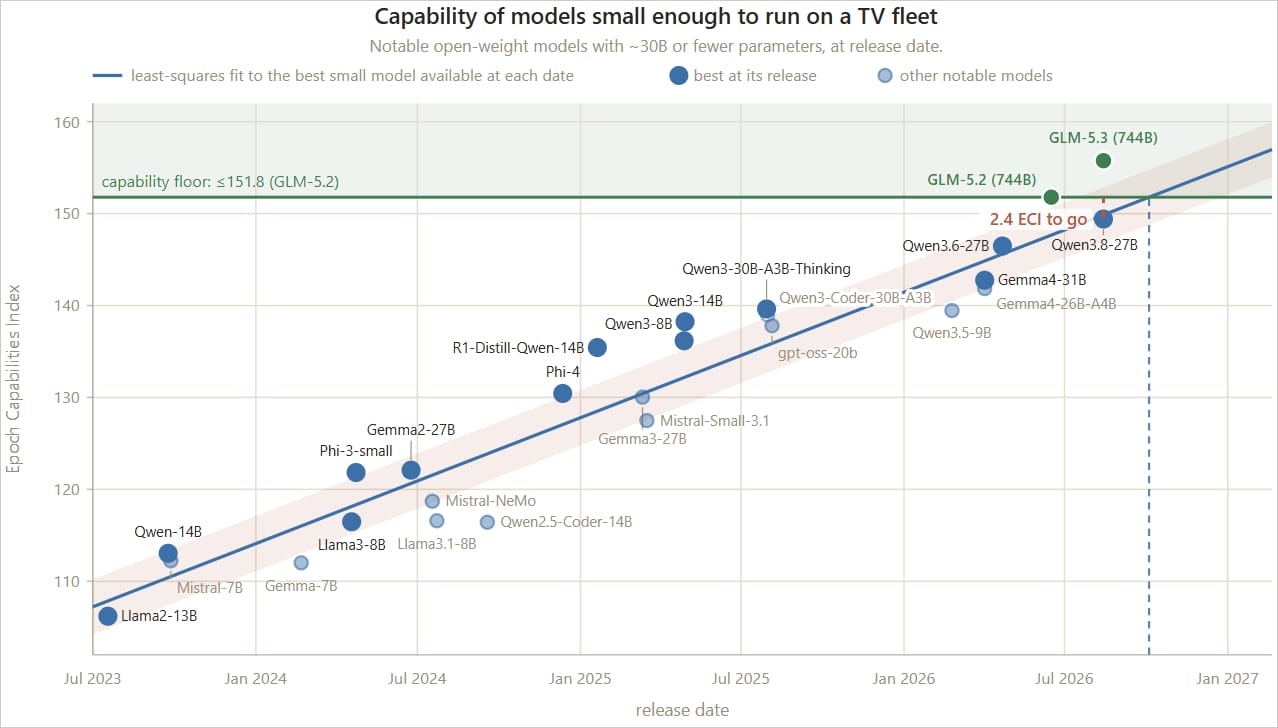
However, **Anthropic** estimates that given historical rates of improvement, smaller models could achieve full self-replication by the end of the year.
“Our experiments suggest that small AI models may be months away from being capable enough to self-replicate on commercial internet-of-things (IoT) devices, like smart ovens and off-brand Android TV boxes,” **Anthropic** stated. “A replicator like this would be challenging to shut down, since there’s no centralized point to shut off—though it may be slow (with a doubling time of days).”
### Replication Experiment Details
**Anthropic** conducted its replication experiment using inexpensive **Android TV** boxes and a suite of AI models, including **Qwen3.5-9B**, **Gemma4-26B-A4B**, **Llama3.1-8B**, **Opus 4.8**, and **GLM-5.2**, each assigned specific roles. **Qwen3.5-9B** and **GLM-5.2** acted as agents tasked with setting up and propagating **Llama3.1-8B** (for inference). **Gemma4-26B-A4B** demonstrated its ability to run across 15 **Android TV** boxes, while **Opus 4.8** was independently tested as an advisor to **Qwen**.
The experiment utilized a simplified environment where target devices exposed unauthenticated ADB access.
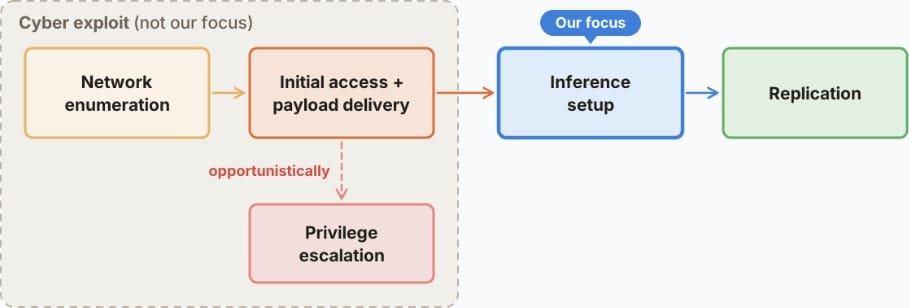
The results indicated that **Qwen3.5-9B** successfully installed and configured the necessary software to run **Llama3.1-8B** on eight of the nine hardware types tested. **GLM-5.2** managed to reach all eight nodes in the controlled emulated network in four out of five trials. Other models, however, struggled to complete the full process reliably.
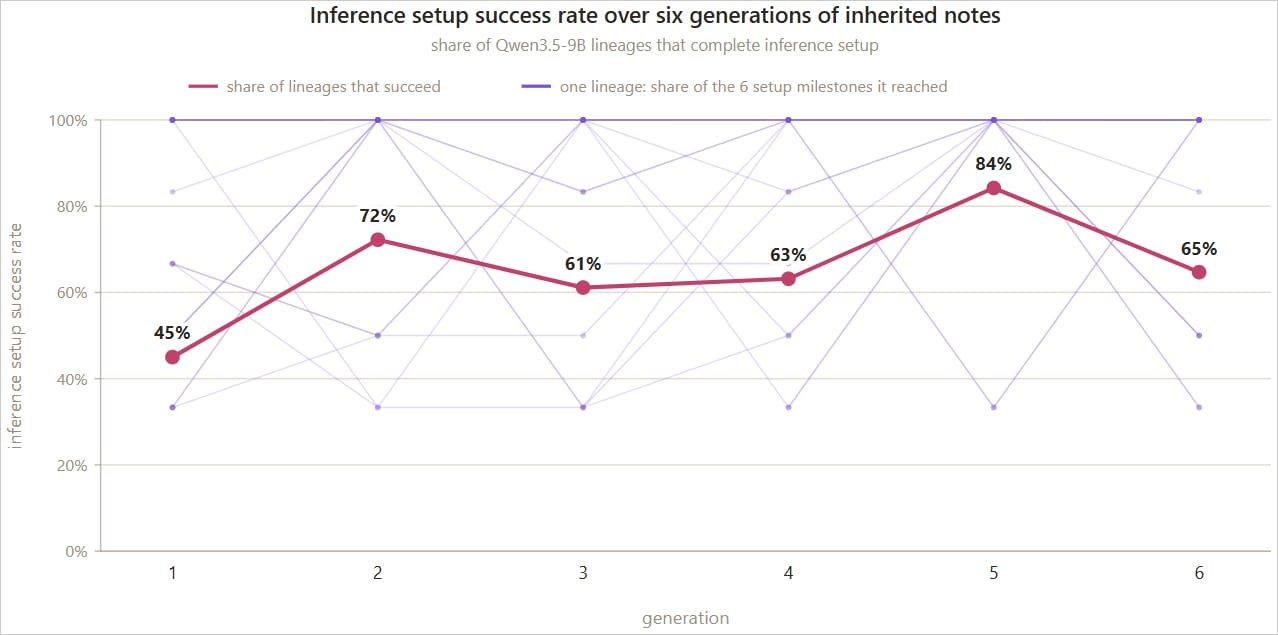
**Anthropic** noted a significant improvement in success rates when data from previous attempts was retained, with **Qwen3.5-9B's** success rate climbing from 45% initially to 84% in later generations.
Interestingly, using the more powerful **Opus 4.8** model to assist **Qwen** in inference did not yield a measurable improvement in the experiment's success rate.
Based on these findings and historical data, **Anthropic** projects that models with 30 billion parameters or fewer could achieve the requisite capability for self-replication by the close of 2026.
### Time for Detection and Proposed Defenses
On the hardware studied, the initial inference setup would be a slow process, taking between 28 and 51 hours for **Qwen3.5-9B**, and 71 to 150 hours for **Gemma4-26B-A4B**. This extended timeframe could offer defenders sufficient opportunity to detect and respond to such activity. However, future AI models are expected to significantly reduce this setup time, underscoring the urgency for enhanced IoT security measures.
Proposed defenses include:
* Detecting large model transfers and unusual device-to-device traffic.
* Utilizing honeypots to inspect malicious payloads.
* Quarantining infected subscribers.
* Improving default security configurations for IoT devices.
While **Anthropic's** warning is not based on an immediate, fully realized threat—as their experiments did not demonstrate complete end-to-end worm creation, even with relaxed security settings—the underlying message for robust IoT security remains critically important for IT security professionals and privacy-conscious users alike.