Cisco Urges Immediate Patching for Critical Secure Email Gateway Zero-Day Under Active Exploitation
Cisco has issued an urgent warning to customers regarding a critical zero-day vulnerability in its **Secure Email Gateway** (SEG) appliances, tracked as **CVE-2026-76461**. Threat actors are actively exploiting this flaw, which allows unauthenticated remote attackers to execute arbitrary commands with root privileges. Organizations are advised to patch immediately to mitigate the severe risk.
Cybersecurity teams are on high alert as **Cisco** confirms active exploitation of a critical zero-day vulnerability, **CVE-2026-76461**, affecting its **Secure Email Gateway** devices.
The flaw, stemming from insufficient validation in the email parsing logic of **Cisco AsyncOS Software**, enables unauthenticated, remote attackers to execute arbitrary commands with root privileges on the underlying operating system. This is achieved by sending a crafted email containing malicious SQL statements.
**Cisco** became aware of the active exploitation in September 2026, prompting an immediate security advisory.
## Understanding the Threat
Successful exploitation of **CVE-2026-76461** grants attackers full control over the compromised SEG appliance. The vulnerability affects both virtual and physical appliances, regardless of their specific configuration.
**Cisco** has provided indicators of compromise (IoCs), urging network defenders to scrutinize `mail_logs` on each cluster device for suspicious SQL statements. Furthermore, administrators are advised to cross-reference network and firewall logs for any signs of suspicious activity, including uploads and downloads to external or malicious IP addresses, as attackers may attempt to remove evidence post-exploitation.
## Widespread Exposure and CISA Alert
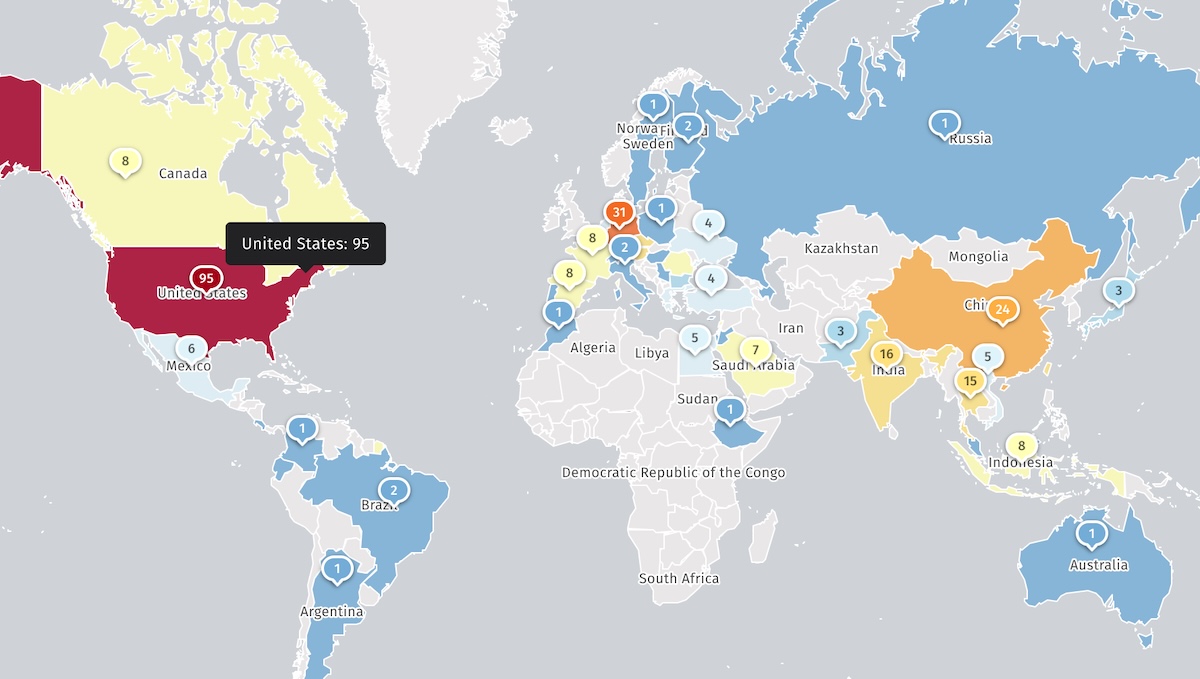
Internet security watchdog **Shadowserver** currently tracks over 400 **Cisco Secure Email Gateway** appliances exposed to the internet, though it does not differentiate between honeypots or patched systems.
The **Cybersecurity and Infrastructure Security Agency (CISA)** has added **CVE-2026-76461** to its **Known Exploited Vulnerabilities (KEV) Catalog**, mandating federal agencies to patch their systems by September 17, underscoring the urgency of this vulnerability.
## Broader Cisco Vulnerabilities
In addition to the zero-day, **Cisco** addressed four other critical vulnerabilities (**CVE-2026-76440**, **CVE-2026-76441**, **CVE-2026-20353**, and **CVE-2026-76443**) affecting **Secure Email Gateway** (SEG) and **Secure Email and Web Manager** (SEWM) appliances. While these are critical, **Cisco** has no evidence of their active exploitation in the wild.
This isn't an isolated incident for **Cisco**. In January, the company patched a maximum-severity **Cisco AsyncOS** flaw (**CVE-2025-20393**) that had been exploited in zero-day attacks against SEG and SEWM devices since November 2025. More recently, **Cisco** revealed that ransomware groups and state-sponsored threat actors exploited two patched **Secure Firewall Management Center** (FMC) flaws.
Since November 2021, **CISA** has flagged 98 **Cisco** vulnerabilities as actively exploited, with seven linked to ransomware operations. This ongoing pattern highlights the critical importance of timely patching and robust security practices for organizations utilizing **Cisco** products.