Convertr E-commerce Platform Targeted in Sophisticated Payment Skimming Attack
A sophisticated payment card skimming operation has compromised **Convertr**, a major Brazilian e-commerce platform, leading to the potential theft of sensitive payment data from shoppers. The attack, attributed to a Brazilian group active since July 2024, leveraged a vulnerable analytics script to inject malicious code directly into checkout pages.
A credit card skimming group has successfully compromised a shared analytics script utilized by the e-commerce platform **Convertr**, enabling them to steal shoppers' payment data during checkout. The campaign, identified on October 24, has been linked to a Brazilian gang with a history of targeting online stores running **Magento**, **OpenCart**, and **WooCommerce** platforms.
**Convertr**, a prominent Brazilian e-commerce platform, powers online stores and checkout systems for numerous major fashion brands in the country, processing an estimated R$2 billion ($370 million) in sales.
E-commerce security firm **Sansec** reported that attackers modified a **Plausible** tracker file hosted on a self-managed server operated by **Convertr**. **Plausible** is an open-source alternative to **Google Analytics**.
**Sansec** suspects the attackers exploited **CVE-2026-8467**, an unauthenticated command-execution vulnerability affecting **Convertr**'s outdated **Plausible Community Edition** installation, to gain initial access. However, this remains unconfirmed.
Upon gaining access, the attackers injected malicious code into a legitimate **Plausible** analytics tracker residing on **Convertr**'s infrastructure. This malicious script subsequently loaded on the checkout pages of all merchants utilizing the platform.
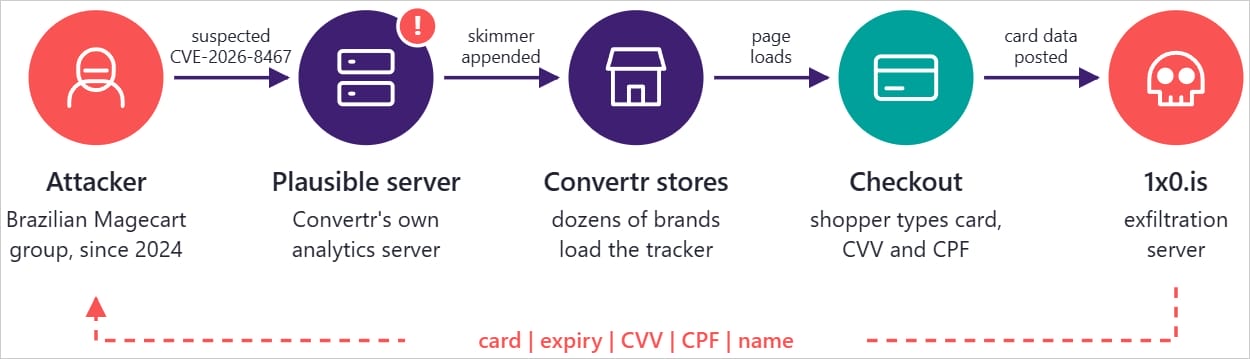
**Sansec** noted that earlier iterations of the skimmer used generic payment-field patterns. By October 26, the attackers deployed a more refined version specifically targeting **Convertr**'s exact payment API field names.
The injected skimmer was configured to exfiltrate the following data types from checkout pages:
* Payment card number
* Expiration date
* CVV code
* Cardholder name
* CPF taxpayer identification number
Researchers advise individuals who made card payments on a Brazilian store displaying 'checkout.convertr' in the checkout page address since October 24 to immediately contact their bank and request a card block.
In an update, **Sansec** confirmed that **Convertr** has since "removed the skimmer and upgraded **Plausible** to a patched version." The company has also announced that it is notifying affected merchants and payment providers.
**Sansec** researchers cautioned that browser caching could potentially keep the malicious script active on impacted sites for up to 24 hours post-cleanup. Customers are therefore advised to clear their browser cache before placing new orders, even after the threat has been remediated.
To enhance payment card security when shopping online, using disposable virtual cards that expire immediately after a transaction is a recommended practice.