F5 BIG-IP APM Zero-Day Under Active Exploitation, Emergency Patches Released
**F5** has issued urgent security updates to address a critical zero-day vulnerability, **CVE-2026-94127**, in its **BIG-IP APM** (Access Policy Manager) solution. This flaw is actively being exploited in remote code execution attacks, prompting immediate action from organizations utilizing the software.
The vulnerability, tracked as **CVE-2026-94127**, affects **BIG-IP APM** instances configured as an **OAuth Authorization Server** when both an **APM** access policy and an **OAuth** profile are configured on a virtual server.
**F5** confirmed the active exploitation in a security advisory, stating, "We have learned that this vulnerability has been exploited." Deployments using **APM** strictly as an **OAuth Client / Resource Server** (without **OAuth** authorization server profiles configured) are not impacted.
Organizations are strongly advised to review their systems for indicators of compromise (IoCs), particularly if they observe a combination of multiple **OAuth** authentication failures and suspicious commands, followed by a **TMM SIGABRT**.
For those unable to apply the security updates immediately, **F5** has provided mitigation measures, which involve implementing an **iRule** (available through **F5 Support**) on the affected **BIG-IP APM** virtual server.
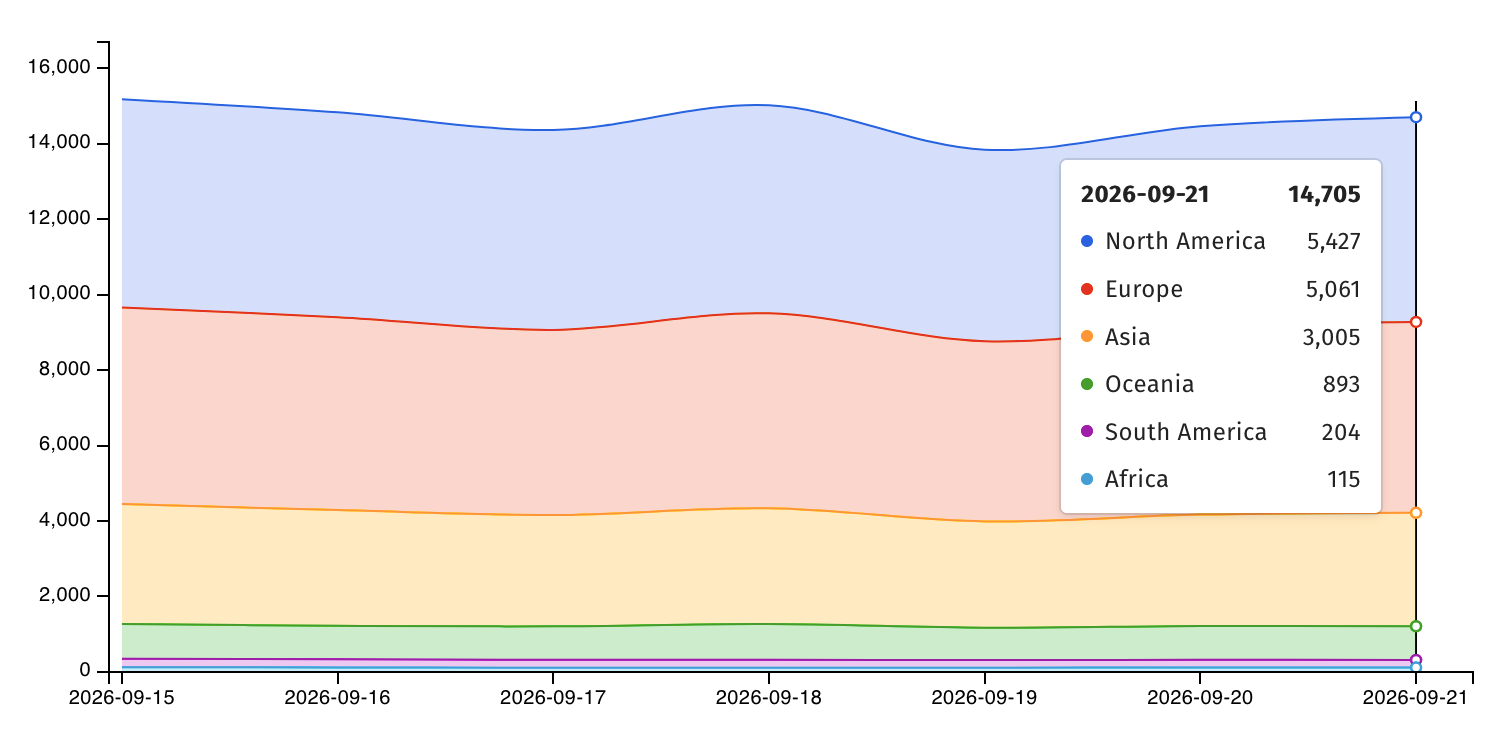
Internet threat monitoring non-profit **Shadowserver** currently identifies over 14,700 **IP** addresses with **BIG-IP APM** fingerprints online. However, it's unclear how many of these have been patched or are honeypots.
### CISA Mandates Federal Action
The **Cybersecurity and Infrastructure Security Agency (CISA)** has added **CVE-2026-94127** to its **Known Exploited Vulnerabilities (KEV) Catalog**. Federal agencies in the U.S. have been ordered to secure their networks against this flaw by Friday.
**CISA** emphasized the severity, warning that "These types of vulnerabilities are a frequent attack vector for malicious cyber actors and pose significant risks to the federal enterprise."
### History of F5 Exploitations
**F5** products have frequently been targeted by cybercrime and state-backed threat groups. In recent years, vulnerabilities in **F5** solutions have been exploited to breach corporate networks, hijack devices, map internal servers, deploy data-wiping malware, and steal sensitive documents.
Notably, **F5** disclosed in October 2025 that state-sponsored hackers had breached its systems in August 2025, exfiltrating undisclosed **BIG-IP** security source code and vulnerabilities. Since November 2021, **CISA** has flagged eight actively exploited **F5** vulnerabilities, with four of them also abused in ransomware attacks.
**F5** is a Fortune 500 company providing cybersecurity and application delivery networking (**ADN**) services to over 23,000 customers globally, including a significant portion of the Fortune 50 and Fortune Global 500.