FBI Seizes NightmareStresser Domains in Latest Blow to DDoS-for-Hire Services
The **U.S. Federal Bureau of Investigation (FBI)** has successfully seized the domains of **NightmareStresser**, one of the longest-running distributed denial-of-service (DDoS) platforms. This action is part of the ongoing international law enforcement initiative, **Operation PowerOFF**, targeting 'booter' services that enable individuals to launch massive DDoS attacks for a fee.
On Tuesday, the **FBI** announced the seizure of the nightmare-stresser[.]com and nightmarestresser[.]org domains. These sites were central to **NightmareStresser**, a prominent DDoS-for-hire service that allowed users to rent botnets of compromised devices to unleash powerful DDoS attacks against various online platforms.
### The Scale of NightmareStresser's Operations
Before its takedown, **NightmareStresser** marketed itself as the "#1 online IP booter" and the "only DDoS tool available 24/7." According to cybersecurity firm **Searchlight Cyber**'s 2023 report, the service boasted over 566,000 registered users and operated 52 dedicated servers. These servers were capable of launching DDoS attacks reaching up to 200 Gbps, targeting both Layer 7 application protocols and Layer 4 TCP/UDP protocols.
Since 2022, **NightmareStresser** was responsible for hundreds of thousands of actual or attempted DDoS attacks globally.

### Operation PowerOFF: A Coordinated Global Effort
The recent enforcement action against **NightmareStresser** was conducted under **Operation PowerOFF**, a collaborative initiative involving international law enforcement agencies. This operation is dedicated to dismantling criminal DDoS-for-hire infrastructures worldwide.
A seizure banner now displayed on the formerly active domains confirms the coordinated effort:
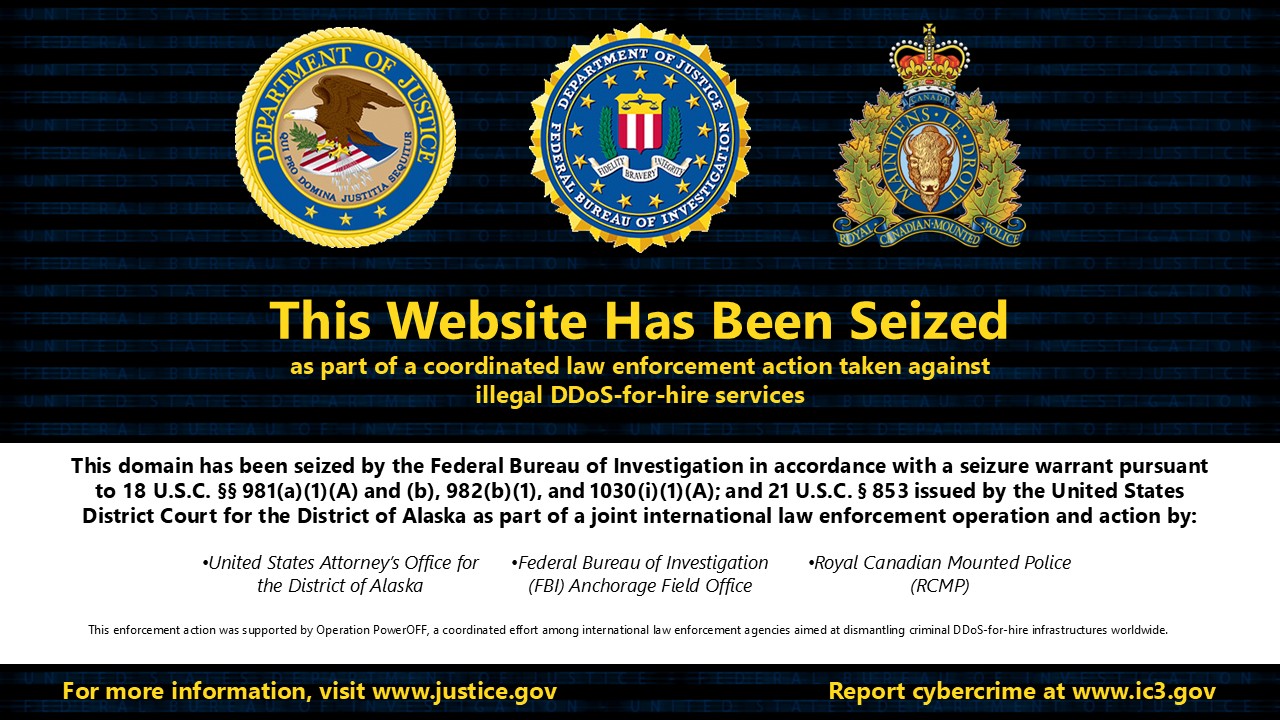
_NightmareStresser seizure banner (BleepingComputer)_
This isn't the first time **NightmareStresser** has faced law enforcement action. In December 2022, the **U.S. Department of Justice (DOJ)** previously took down nightmarestresser[.]com and arrested six suspects allegedly linked to multiple DDoS-for-hire services.
### A History of Disruption
**Operation PowerOFF** is a long-running joint law enforcement action that commenced in December 2018 with the seizure of 15 websites offering DDoS-as-a-service platforms. The operation has since achieved significant successes, including:
* The takedown of the **DigitalStress** DDoS-for-hire service in the United Kingdom.
* The seizure of the **Dstat.cc** DDoS review platform and the arrest of two suspects in Germany.
* The arrest of two stresser service operators in Poland.
In additional joint actions, law enforcement has seized multiple waves of domains, including 13 and then 48 more domains hosting booter platforms. Last year, Polish authorities detained four suspects connected to six DDoS-for-hire platforms responsible for thousands of attacks targeting schools, government services, businesses, and gaming platforms. Concurrently, the U.S. seized nine domains as part of the same coordinated crackdown.
These ongoing efforts underscore the commitment of international law enforcement to disrupt and dismantle the illicit market for DDoS-for-hire services, enhancing online security for users and organizations worldwide.