Over 1,000 GitLab Servers Remain Vulnerable to Actively Exploited RCE Flaw
Despite patches released three weeks ago, over 1,000 internet-exposed **GitLab** servers are still unpatched against a critical remote code execution (RCE) vulnerability, **CVE-2026-97229**. This maximum-severity flaw is actively being exploited in the wild, posing a significant risk to organizations using self-managed **GitLab** instances.

## Critical GitLab RCE Flaw Under Active Exploitation

More than 1,000 internet-exposed **GitLab** servers are reportedly still vulnerable to **CVE-2026-97229**, a maximum-severity flaw that is currently being exploited in remote code execution (RCE) attacks. This vulnerability stems from an integer overflow weakness found in the CI/CD Regular Expression Compiler, which processes regular expressions within pipeline configuration files.
**GitLab** addressed this issue on October 12, releasing security patches for **GitLab Community Edition (CE)** and **Enterprise Edition (EE)** versions 19.4.2, 19.3.5, and 19.2.8. The company urged all self-managed **GitLab** installations to upgrade immediately, emphasizing that **GitLab.com** and **GitLab Dedicated** customers were already secured.
## CISA Confirms In-the-Wild Exploitation
Last Friday, the **US Cybersecurity and Infrastructure Security Agency (CISA)** confirmed active exploitation of **CVE-2026-97229**, adding it to its **Known Exploited Vulnerabilities (KEV) Catalog**. Federal agencies were given a strict deadline to patch their servers.
Despite these urgent warnings and the availability of patches, threat watchdog **Shadowserver** reported over the weekend that it continues to track more than 1,000 unpatched **GitLab** servers exposed to ongoing attacks.
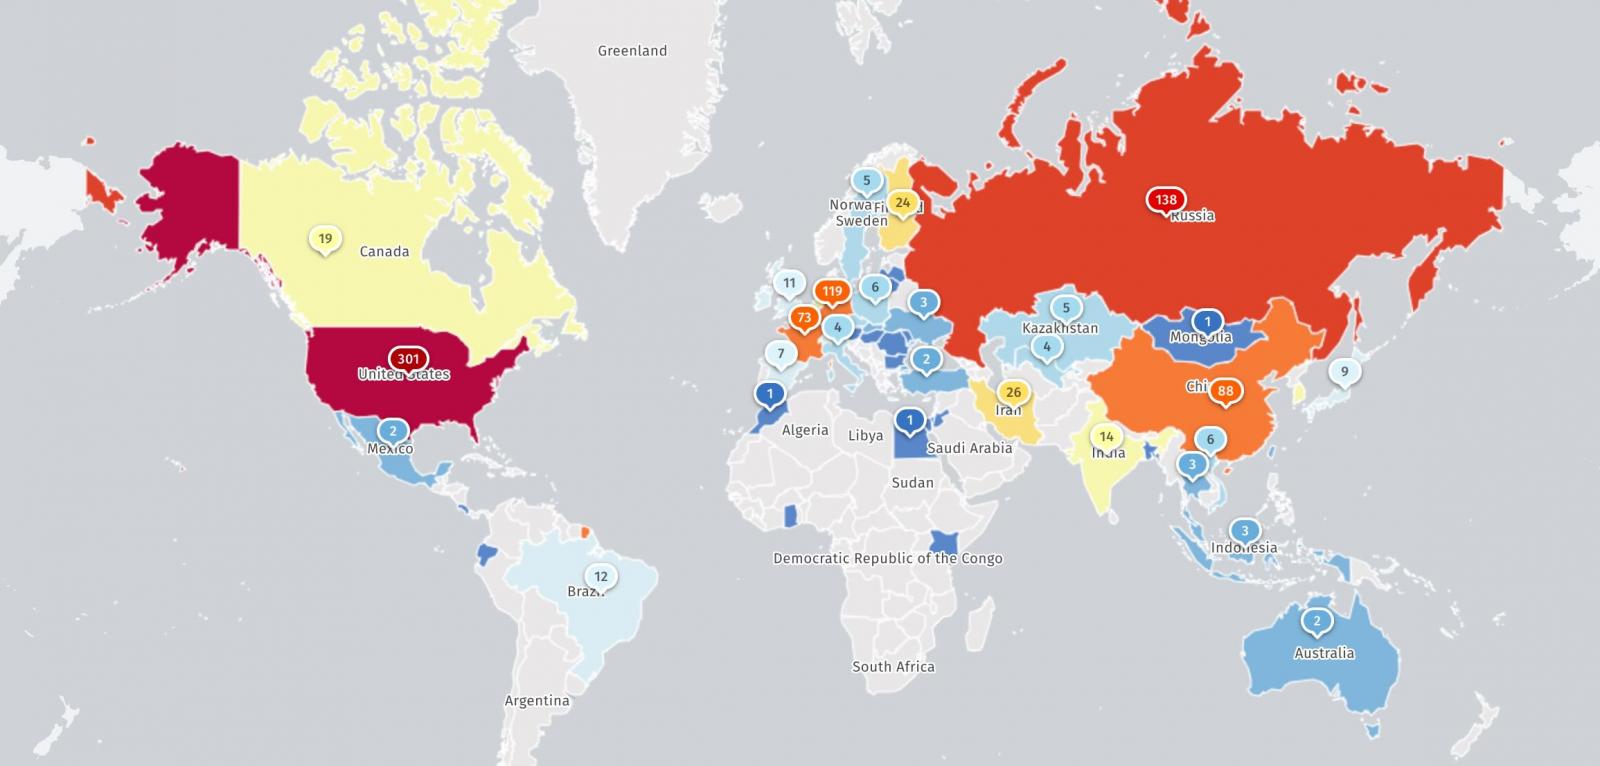
*Vulnerable GitLab instances exposed online (Shadowserver)*
## A History of Critical GitLab Vulnerabilities
**CVE-2026-97229** is the latest in a series of critical security issues affecting **GitLab** this year. In January, a high-severity flaw (**CVE-2026-0723**) allowed attackers to bypass two-factor authentication. September saw another maximum-severity vulnerability (**CVE-2026-85706**) in the repository commits API, which could be exploited to steal credentials and other sensitive data. **CISA** also flagged **CVE-2026-85706** as actively abused in the wild.
Just last month, **GitLab** patched another maximum-severity Regular Expression Compiler bug (**CVE-2026-110264**), enabling threat actors to execute arbitrary code on targeted instances. **Shadowserver** noted on Sunday that over 11,300 instances remain vulnerable to **CVE-2026-110264** out of approximately 39,000 daily-observed **GitLab** instances.
Since November 2021, **CISA** has added six **GitLab** flaws to its **KEV Catalog**, with one even being leveraged in ransomware attacks. Given that **GitLab** boasts over 70 million registered users and is utilized by more than 50% of Fortune 100 companies, the imperative for immediate patching cannot be overstated.