GMO Group Urges Disconnection Amid Ransomware Threat and Data Leak
Japan's **GMO Group**, a major internet services provider, issued an urgent directive for customers to disconnect and shut down PCs following a cyberattack on its **Onamae Desktop Cloud** VPS service. The incident escalated from a potential malware infection to a data breach and a ransomware threat, with the attackers demanding ¥8 billion ($50 million). While the ransomware attack was ultimately averted, customer and company data has been published online.

**GMO Group** has been at the center of a significant cybersecurity incident, urging its **Onamae Desktop Cloud** customers to take drastic measures by disconnecting their systems from the internet and shutting down computers. This came after a threat actor, who had successfully breached the company's VPS provider, threatened to launch a widespread ransomware attack.
### Initial Breach and Malware Concerns
The cyberattack, initially detected on October 20, involved an intrusion that could have installed malware on up to 26,739 customer servers. In response, the company took immediate action, shutting down affected servers and reducing service availability to contain the threat and launch an investigation.
While **GMO Internet** assured customers that payment information remained secure, it warned that **MetaTrader 4** and **MetaTrader 5** (MT4/MT5) credentials and trading-account details might have been exposed. Customers were strongly advised to reset their passwords and terminate all active sessions.
### Ransom Demand and Data Leak
Subsequent updates from **GMO Group** confirmed the theft of data. The attackers demanded a ransom of ¥8 billion ($50 million), which the company publicly refused to pay. Instead, **GMO** announced it would offer ¥5,000 ($30) in compensation to each affected customer for the inconvenience.
On October 26, the company warned that the threat actors planned to leak customer information online and activate a ransomware payload previously planted on customer servers.
### Urgent Disconnection Order
The situation escalated further on October 27, when **GMO Group** issued an urgent plea for customers to disconnect their PCs from the internet, shut them down, and unplug all cables before noon. This drastic measure was taken as the company collaborated with **Trend Micro** to mitigate the ongoing cyberattack.
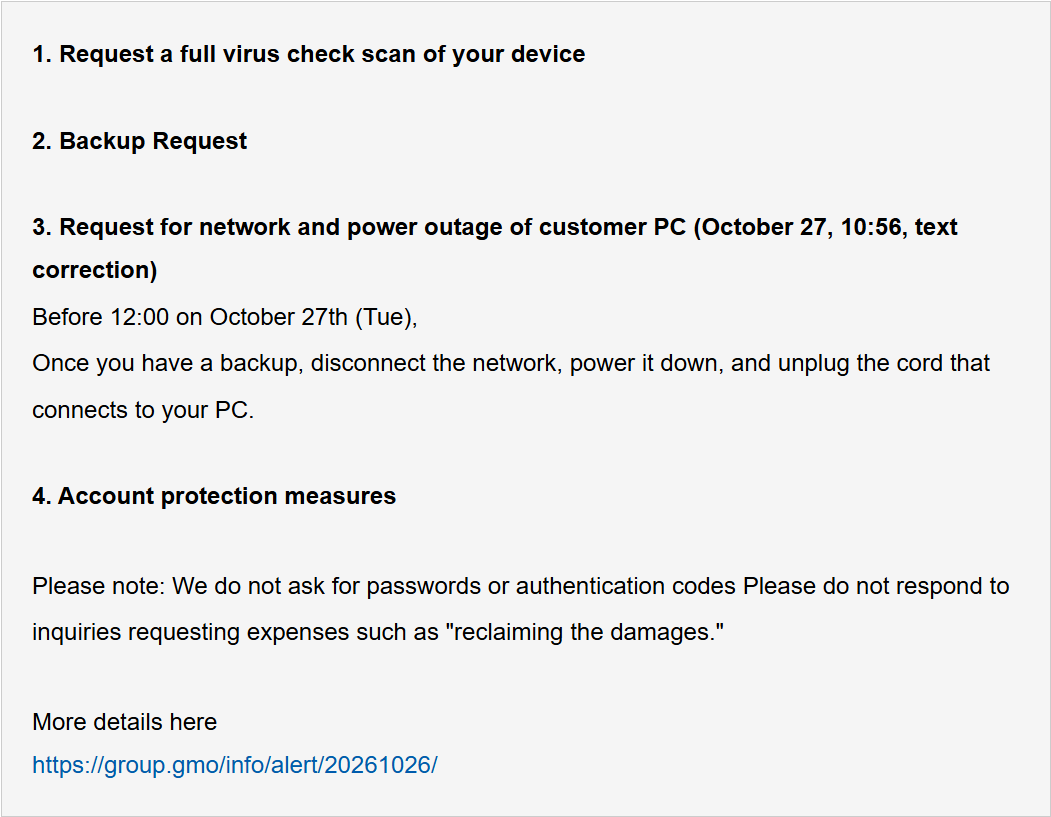
**Instructions to customers**
*Source: GMO*
The company initiated scans of customer systems to detect any lingering malware and offered equivalent PC replacements to those who might suffer damages from a ransomware attack.
### Data Published, Ransom Averted
Later that day, **GMO** confirmed that the threat actor had published company and customer data online, prompting an ongoing effort to verify the authenticity and scope of the leaked information. For customers whose data was exposed, the company stated it would consider additional financial compensation.
Despite the threats, it appears the promised ransomware activation on customer machines never materialized. **GMO Group** has since warned individuals and media against disseminating the exposed information, stating it will pursue legal action against those who do, while reaffirming its steadfast refusal to pay the attackers.