HBO Max Reddit Account Hijacked in 'PasteSwitch' ClickFix Malware Campaign
The official Reddit account for **HBO Max** was compromised and used to distribute malicious advertisements, leading users to a sophisticated 'ClickFix' operation. This campaign, dubbed 'PasteSwitch' by researchers, tricked victims into executing commands that installed information-stealing malware on both Windows and macOS systems. The incident highlights the growing threat of social engineering tactics combined with advanced malware delivery methods.
Hackers recently gained control of **HBO Max**'s verified Reddit account, **u/hbomax**, leveraging it to push over 100 malicious advertisements within a 48-hour window. These ads were part of a larger, multi-platform operation known as **PasteSwitch**, which uses a social engineering technique called 'ClickFix' to deliver information-stealing malware.
Security researchers at **Hudson Rock** and **ADAMnetworks** meticulously analyzed the campaign, revealing its intricate methods for compromising user systems. While some ads mimicked **HBO Max** promotions, others impersonated legitimate AI tools, developer software, and macOS utilities, broadening the attack's potential victim pool.
### The ClickFix Deception
The 'ClickFix' technique is a cunning social engineering ploy. It manipulates users into copying and pasting malicious commands into their operating system's native tools, such as Windows Run, PowerShell, or macOS Terminal. This is often done under the guise of fixing an error, verifying a CAPTCHA, or installing what appears to be legitimate software.
This method is particularly effective because victims voluntarily execute the commands, potentially bypassing traditional browser and security software defenses designed to detect malware downloads.
### Unpacking the PasteSwitch Operation
**PasteSwitch** is a broad campaign targeting both Windows and macOS users. Researchers named it for its core mechanics: attackers provide commands for victims to paste (**PasteSwitch**), and the backend dynamically switches between various campaigns, platforms, payloads, and cryptocurrency theft methods based on the visitor's profile.
This adaptable approach allows the attackers to distribute a wide array of malicious payloads, including information stealers, loaders, cryptocurrency clippers, and fake cryptocurrency wallet applications.
**BleepingComputer** reached out to **HBO** and **Warner Bros. Discovery** for comments regarding the incident but had not received a response at the time of publication.
### Fake HBO Max App Delivers Malware
The compromise was initially uncovered when a Reddit user identified an advertisement from the official **HBO Max** account promoting a non-existent native macOS application for the streaming service.
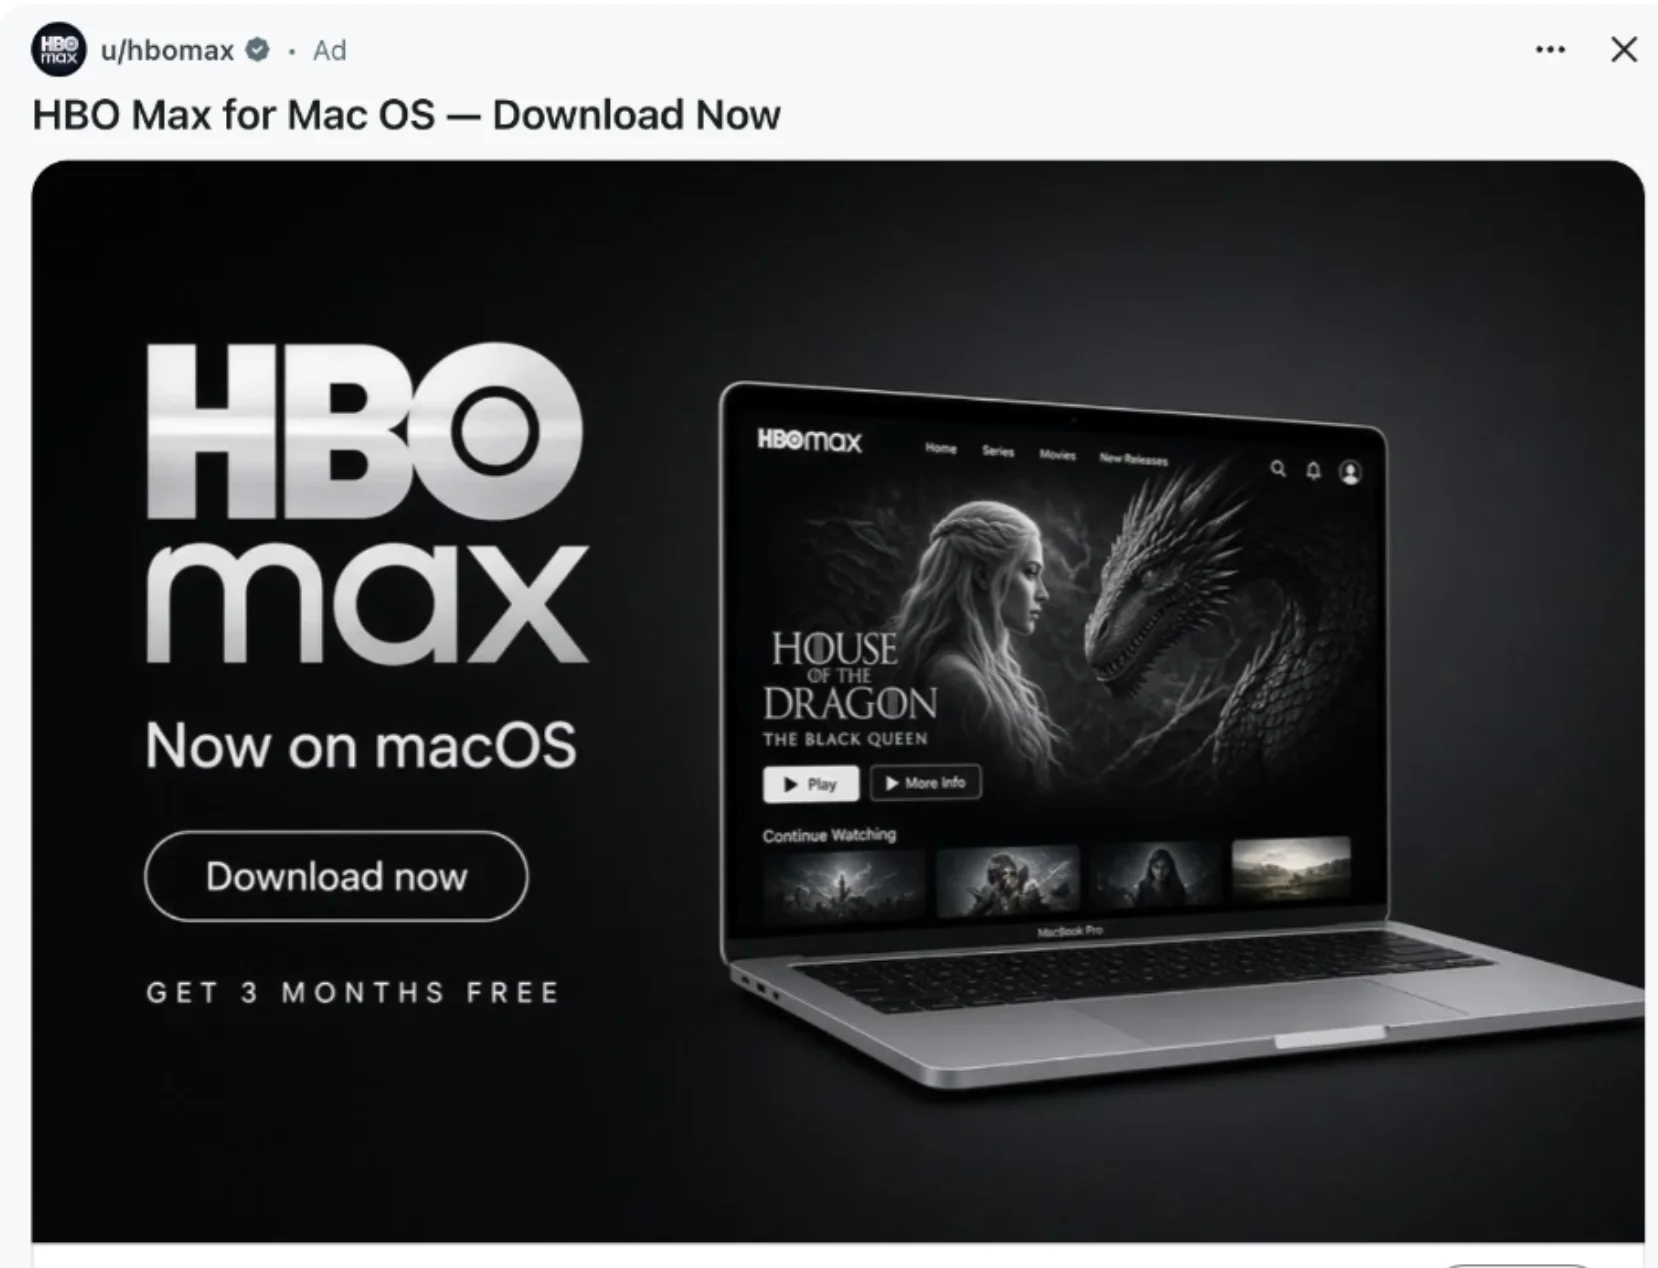
*Malicious HBO Max advertising on Reddit (Source: Adam Networks)*
The Reddit user, posting in **r/cybersecurity**, warned: "I was browsing Reddit and saw an ad displaying u/hbomax as the author - this advertised a macOS HBO Max app which I'd not heard of and was interested in. The user is verified and appears to have posted many times in the official HBO Max subreddits."
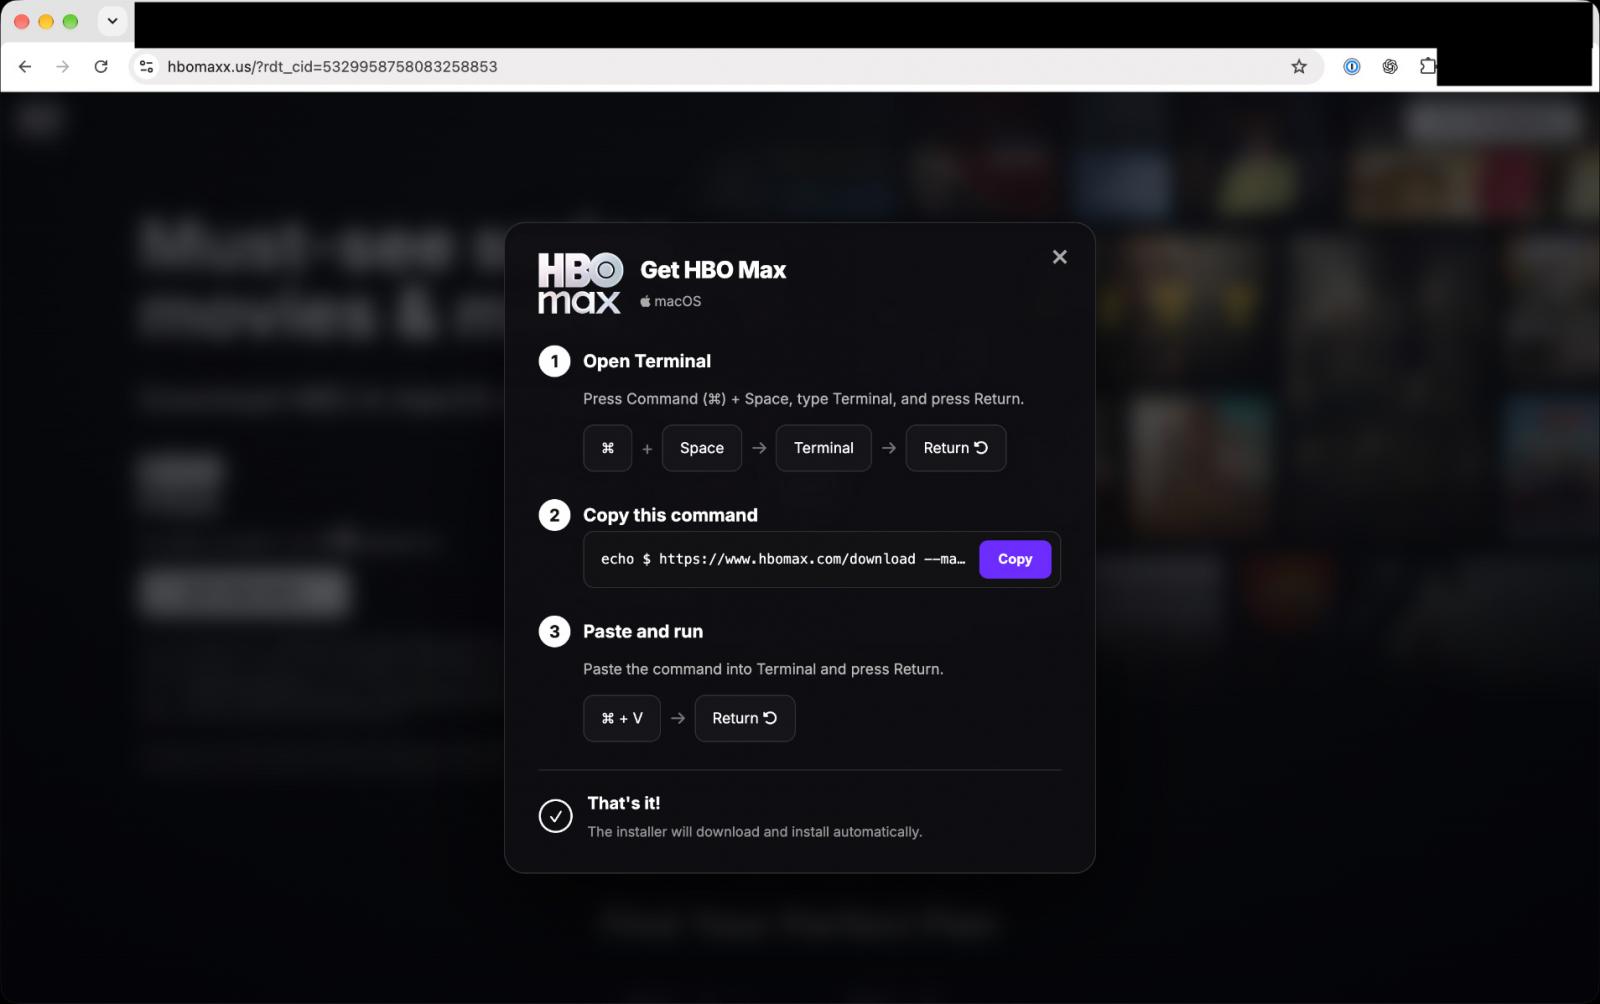
Clicking on these malicious ads redirected users to convincing fake **HBO Max** websites, such as `hbomaxx[.]us`, which mimicked the legitimate service and claimed to offer the application for download.
However, instead of downloading an app, users were presented with instructions to open Terminal and paste a command to install the software.
One macOS command observed in this attack utilized Base64 encoding to obfuscate its true intent. When decoded, it revealed a command to download and execute a script from `ember-bridge[.]com/curl/a44a37519au/setup.sh`.
**Hudson Rock** has previously identified `ember-bridge[.]com` as infrastructure used in September for malware delivery within the **PasteSwitch** operation.
### Malware Payloads and Persistence
Among the malware families deployed in this attack is **MacSync**, which **Hudson Rock** states is capable of stealing browser credentials, Firefox profiles, Telegram data, Apple Notes, and macOS passwords. Another attack chain deployed "**AMOS helper**," which establishes persistence using a directory named `.com.apple.accountsd` and enrolls infected systems with attacker-controlled servers for further tasks.
The campaign also distributed fake cryptocurrency wallet applications for **Ledger**, **Trezor Suite**, and **Exodus**, designed to pilfer victims' wallet recovery phrases.
On Windows systems, **PasteSwitch** has been observed using `mshta` and **PowerShell** to execute commands. One notable Windows attack chain involved an MP3/HTA polyglot to create a scheduled task, launch 32-bit **PowerShell**, disable **Microsoft**'s **Antimalware Scan Interface (AMSI)**, and generate victim-specific infrastructure. Later stages used obfuscated **PowerShell** and shellcode to load the **Amatera Stealer** directly into memory.
Furthermore, **PasteSwitch** has been seen pushing cryptocurrency clipboard hijacking malware, including **AnimateClipper** and **ZigClipper**.
### Broader Advertising Campaign
The **HBO Max** advertisement was merely one facet of a much larger advertising operation run through the compromised Reddit account. Researchers identified numerous ads pointing to various malicious domains:
* 40 ads pointing to `hbomaxx[.]app`
* 36 promoting the fake AI and developer site `codex-craft[.]com`
* 15 promoting `apple.clean-disk-guide[.]com`
* 11 pointing to `code-desktop[.]com`
* 6 promoting `hbomax-macos[.]com`
This diverse targeting strategy allowed the attackers to reach a broader audience, extending beyond just **HBO Max** users to include developers and individuals seeking AI software or system utilities.
After the malicious advertisements were reported, a Reddit admin intervened, pausing the ads and escalating the issue to Reddit's Security and Safety teams. The method by which the attackers gained access to the **HBO Max** Reddit account, and whether other **HBO** or **Warner Bros. Discovery** accounts or systems were affected, remains undisclosed.