High-Severity Roundcube Webmail Flaw Now Under Active Exploitation
A critical SQL injection vulnerability in **Roundcube Webmail**, initially patched in May, is now being actively exploited in the wild. This flaw, **CVE-2026-48842**, poses a significant threat to the thousands of services and millions of users relying on this popular email client, enabling pre-authentication bypass and data theft.

A high-severity vulnerability within **Roundcube Webmail**, a widely used browser-based IMAP email client, is now being actively exploited, according to the **Canadian Centre for Cyber Security**. This flaw, tracked as **CVE-2026-48842**, was originally patched in May.
**Roundcube Webmail** serves as the default mail interface for thousands of services and millions of users, often pre-installed with the popular **cPanel** web hosting control panel.
### The Vulnerability: CVE-2026-48842
In May, the **Roundcube** security team addressed **CVE-2026-48842**, describing it as a pre-authenticated SQL injection within the `virtuser_query` built-in plugin. This plugin is responsible for handling database-driven user lookups and mapping users to email addresses.
Successful exploitation of this vulnerability allows threat actors, even without any prior privileges, to bypass authentication, inject and execute malicious database commands, and steal data from **Roundcube**'s database. These attacks are high-complexity and do not require user interaction.
**Roundcube** strongly recommended that users update their servers to versions 1.6.16 and 1.7.1 to mitigate this vulnerability.
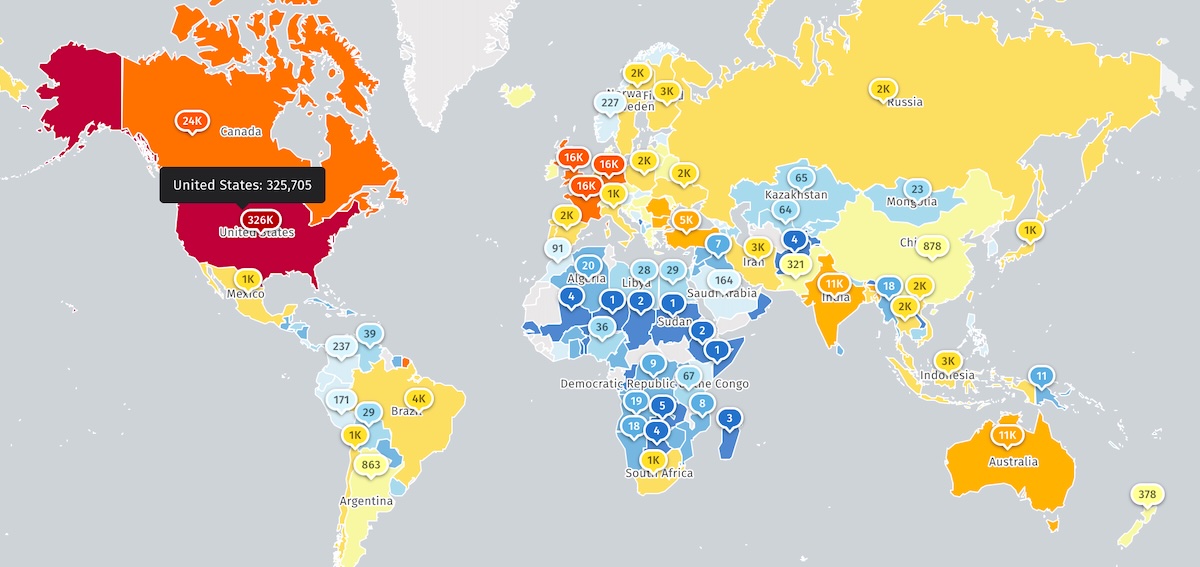
Threat monitoring non-profit **Shadowserver** currently tracks over 523,000 **Roundcube** instances exposed on the internet. However, it's unclear how many of these are honeypots or have already been patched.
### Active Exploitation Confirmed
Four months after the initial patch, the **Canadian Centre for Cyber Security** updated its May advisory, confirming that attackers are now actively exploiting **CVE-2026-48842** in the wild.
"Open-source reporting indicates that **CVE-2026-48842** is being exploited in the wild," the **Cyber Center** warned, urging administrators to secure their webmail servers immediately.
For administrators unable to promptly upgrade their servers, disabling or removing the `virtuser_query` plugin is recommended as an interim measure to eliminate the attack vector.
### A History of Targeted Exploitation
**Roundcube** security flaws have historically been a prime target for both cybercrime groups and state-backed hacking operations. Notably:
* The Russian threat group **Winter Vivern (TA473)** exploited a cross-site scripting (XSS) zero-day (**CVE-2023-5631**) in attacks targeting European government entities.
* The Russian cyber-espionage group **APT28** leveraged multiple flaws (**CVE-2020-35730**, **CVE-2020-12641**, and **CVE-2021-44026**) to breach Ukrainian government email systems.
More recently, in February, the **U.S. Cybersecurity and Infrastructure Security Agency (CISA)** flagged two other **Roundcube** flaws (**CVE-2025-49113** and **CVE-2025-68461**) as actively exploited, mandating government agencies to secure their networks within three weeks.
Since May 2022, **CISA** has identified 11 **Roundcube Webmail** vulnerabilities as being exploited in the wild, underscoring the persistent threat associated with this platform.