Ivanti Patches Two More Connect Secure Zero-Days Exploited in the Wild
Ivanti has released urgent security updates for its Connect Secure (ICS) remote access gateways, addressing two new zero-day vulnerabilities. These flaws, tracked as **CVE-2026-111357** and **CVE-2026-118527**, have been actively exploited in conjunction with an authentication bypass vulnerability, **CVE-2026-104935**, since at least October 1.


**Ivanti** has issued critical patches for two additional zero-day vulnerabilities affecting its **Connect Secure (ICS)** remote access gateways. These newly disclosed flaws, **CVE-2026-111357** (a high-severity privilege escalation) and **CVE-2026-118527** (allowing authenticated attackers to upload files), have been actively exploited in the wild since October 1.
### Chained Exploitation
Threat actors have been chaining these vulnerabilities with **CVE-2026-104935**, an authentication bypass flaw that **Ivanti** patched last month. This chaining allows for unauthenticated root-level code execution on affected **ICS** devices.
When **CVE-2026-104935** was initially addressed in October, **Ivanti** urged administrators to upgrade immediately, acknowledging "limited exploitation in the wild." The company stated their initial focus was on quickly resolving the primary exploitation path of **CVE-2026-104935**.
### Discovery and Tactics
Cybersecurity firm **Volexity** first identified the exploitation, reporting that a threat actor, designated **UTA0576**, was chaining **CVE-2026-104935** with two other undisclosed flaws since October 3. Notably, **UTA0576** did not deploy traditional malware or web shells. Instead, the attackers re-exploited the device for each command and tampered with logs to evade detection by **Ivanti**'s Integrity Checker Tool.
Threat intelligence firm **Defused** corroborated these findings, observing active exploitation of **CVE-2026-104935** as early as October 1.
### CISA Warning and Exposure
Earlier this week, the **US Cybersecurity and Infrastructure Security Agency (CISA)** added **CVE-2026-104935** to its catalog of actively exploited vulnerabilities, mandating federal agencies to patch their systems by Friday.
Internet threat watchdog **Shadowserver** currently tracks over 5,000 Internet-exposed **ICS** instances. The number of these instances that have been secured against the ongoing attacks remains unclear.
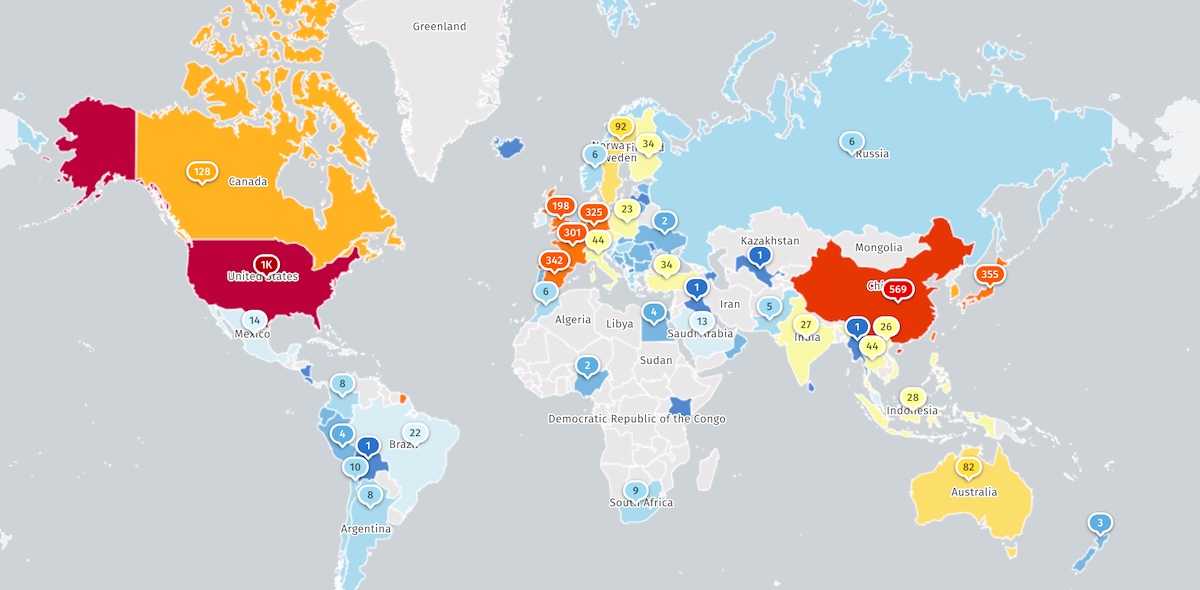
*Internet-exposed Ivanti ICS instances (Shadowserver)*
### A Pattern of Exploitation
**Ivanti** vulnerabilities are frequently targeted by threat actors, often in zero-day attacks, due to their potential to provide quick access to enterprise networks for data exfiltration. Over the past several years, **Ivanti** has patched numerous **Connect Secure** zero-days, some of which have been used in widespread campaigns to deploy custom malware.
Recent examples include a command injection (**CVE-2024-21887**) and an authentication bypass (**CVE-2023-46805**) patched in January 2024, followed by a server-side request forgery (**CVE-2024-21893**) two weeks later. More recently, remote code execution (RCE) bugs **CVE-2025-0282** and **CVE-2025-22457** were addressed in January and March 2025, respectively, with the latter exploited by China-linked state hackers.
Since November 2021, **CISA** has flagged 38 **Ivanti** vulnerabilities as actively exploited, including 12 that have been leveraged in ransomware attacks. **Ivanti** boasts over 3,000 employees, 7,000 partners, and 40,000 customers globally.