JadePuffer Ransomware Unleashes AI Agents to Devastate Azure Cloud Resources
The **JadePuffer** ransomware group is leveraging sophisticated AI agents to execute destructive attacks against **Azure** tenants. These agent-driven operations conduct reconnaissance, steal credentials, and systematically destroy critical cloud infrastructure, highlighting an evolving threat landscape for cloud security professionals.

New reports reveal that the **JadePuffer** ransomware operator is actively targeting **Azure** tenants with highly automated, agent-driven attacks. These advanced operations are designed to conduct extensive reconnaissance, exfiltrate credentials, and ultimately obliterate core cloud components.
First emerging in July, **Sysdig** researchers initially highlighted **JadePuffer**'s innovative use of AI agents to automate the entire attack chain. This includes everything from initial reconnaissance and credential theft to lateral movement, persistence, and data encryption.
Subsequently, **Sysdig** noted an expansion in **JadePuffer**'s focus. The threat actor began targeting AI assets, training datasets, and vector databases, deploying a specialized tool named **EncForge** for these operations.
## Microsoft's Observations: Destructive Operations in Azure
**Microsoft Security Research** recently detailed two **JadePuffer** attacks observed in June. These incidents involved mapping cloud resources, retrieving storage account keys, and ultimately deleting numerous **Azure Storage** accounts.
The destructive phase of these attacks was remarkably swift, lasting only seven minutes. During this brief window, the threat actor targeted over 100 storage accounts, alongside **Key Vaults**, **Function Apps**, **Virtual Machines**, and **App Services**.
Despite the attacker's destructive intent, some targeted **Azure Storage** accounts remained unaffected. This resilience was attributed to existing **Azure** resource locks and storage account-level protections.
**Microsoft** tracks the **JadePuffer** threat actor as **Storm-3168**. The attacks were executed using two compromised service principals – security identities that allow applications and automated tools to authenticate and access assigned **Azure** resources. Both service principals belonged to the same tenant, with one dedicated to reconnaissance and resource discovery, and the other performing discovery, destructive actions, and credential collection.
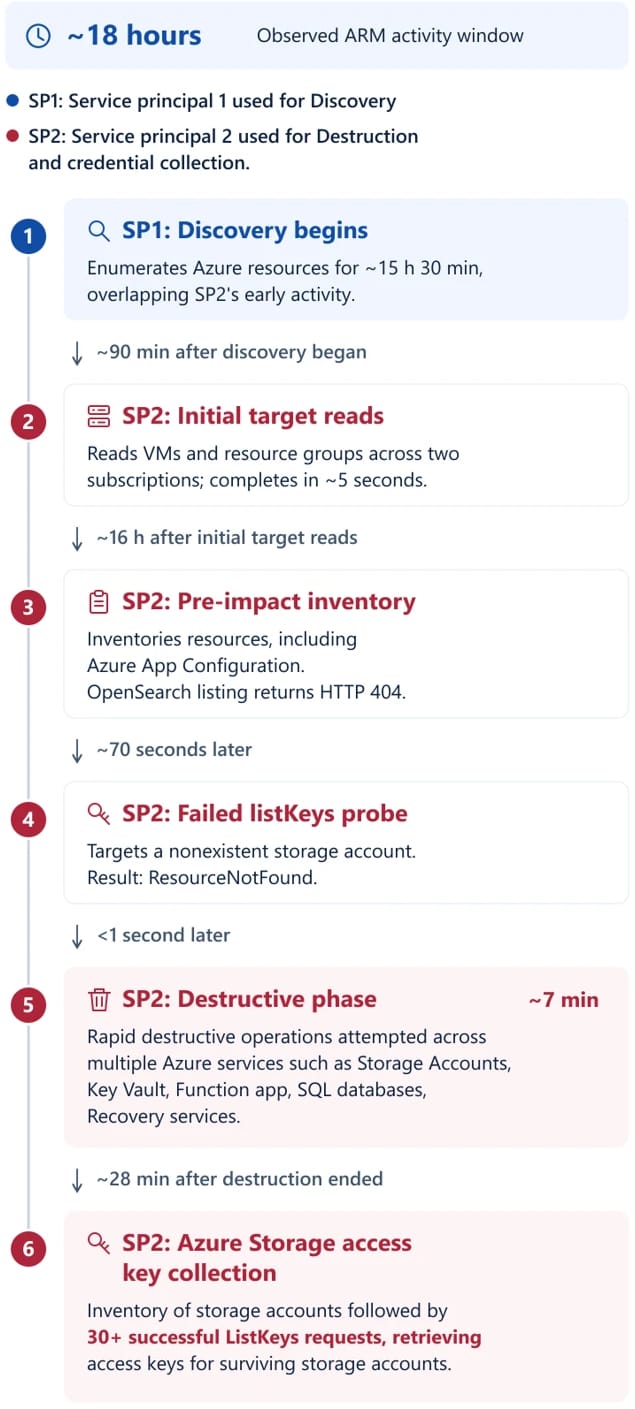
Crucially, the attacker also attempted to remove backup and recovery protections, specifically **Azure Site Recovery** locks. This tactic suggests an effort to hinder restoration capabilities, potentially bolstering ransomware extortion efforts, although **Microsoft** did not confirm financial demands or data theft in these specific observed cases.
Attempts to delete **Azure SQL** databases failed due to the attacker using an unsupported API version. Similarly, efforts to remove recovery protection locks were unsuccessful.
**Microsoft** commented on this multi-service targeting, stating, “The parallel targeting of **Azure SQL** databases and storage accounts suggests an effort to broaden the destructive impact across different data services rather than concentrating on a single resource type.”
Approximately 30 minutes after the initial wipe attempts, **Storm-3168** returned to execute over 30 requests for storage account keys, most of which proved successful.
## Initial Access and Mitigation
While **Microsoft** could not definitively determine the initial access vector, researchers noted that credentials for one of the compromised service principals were found in a public **GitHub** issue prior to the attacks.
To mitigate similar threats, **Microsoft** recommends several key steps for system administrators:
* Activating cloud workload protections.
* Diligently checking for secrets exposed in public repositories.
* Routinely evaluating **Azure RBAC** permissions against least-privilege principles.
These incidents underscore the critical need for robust cloud security postures and continuous vigilance against increasingly sophisticated, AI-driven threats.