Kiteworks Lifts Precautionary Shutdown After Patching Critical Vulnerability
Secure file-sharing provider **Kiteworks** (formerly **Accellion**) has rescinded a global advisory urging customers to temporarily shut down their systems. The move follows the successful patching of a critical, undisclosed vulnerability and an absence of any evidence of compromise after a warning from federal intelligence authorities.
American tech company **Kiteworks** has lifted a precautionary advisory that requested customers power down their systems. This action was taken after the company successfully patched a critical, unnamed vulnerability.
**Kiteworks**, known for its Private Content Network (PCN) which integrates enterprise email, file sharing, Managed File Transfer (MFT), APIs, and web forms, serves thousands of global corporations and government agencies, with over 100 million end-users.
Last Saturday, the secure file-sharing software company urged customers worldwide to temporarily shut down their servers. This recommendation came after receiving a warning from federal intelligence authorities about a potentially imminent cyberattack.
By Monday, **Kiteworks** had brought all hosted customer systems back online. The company reported finding no evidence of compromise or suspicious activity during the precautionary shutdown.
"Continuous monitoring throughout the period showed no abnormal activity, and the company has no indication that any **Kiteworks** or customer system was compromised," **Kiteworks** stated.
An update to the original advisory confirmed, "As of September 27th, the shutdown recommendation is now lifted for all customers. If you have not already restarted, you may bring your **Kiteworks** system back online."
The critical vulnerability was identified in a feature utilized by less than 1% of **Kiteworks**' customer base. The company advised customers using self-hosted **Kiteworks Advanced Forms** to contact support for further assistance.
"**Kiteworks** developed and deployed a fix during the window, applied an additional protective layer across all environments, and has no indication the vulnerability was ever exploited. All other **Kiteworks** products were unaffected," the company noted.
Details regarding the patched vulnerability, including a **CVE** ID, have not yet been publicly released by **Kiteworks**.
Threat monitoring service **Shadowserver** has identified nearly 400 **Kiteworks** instances accessible via the internet, with 234 of these located in the United States. **Shadowserver** did not provide information on how many of these instances might be honeypots or have already been patched.
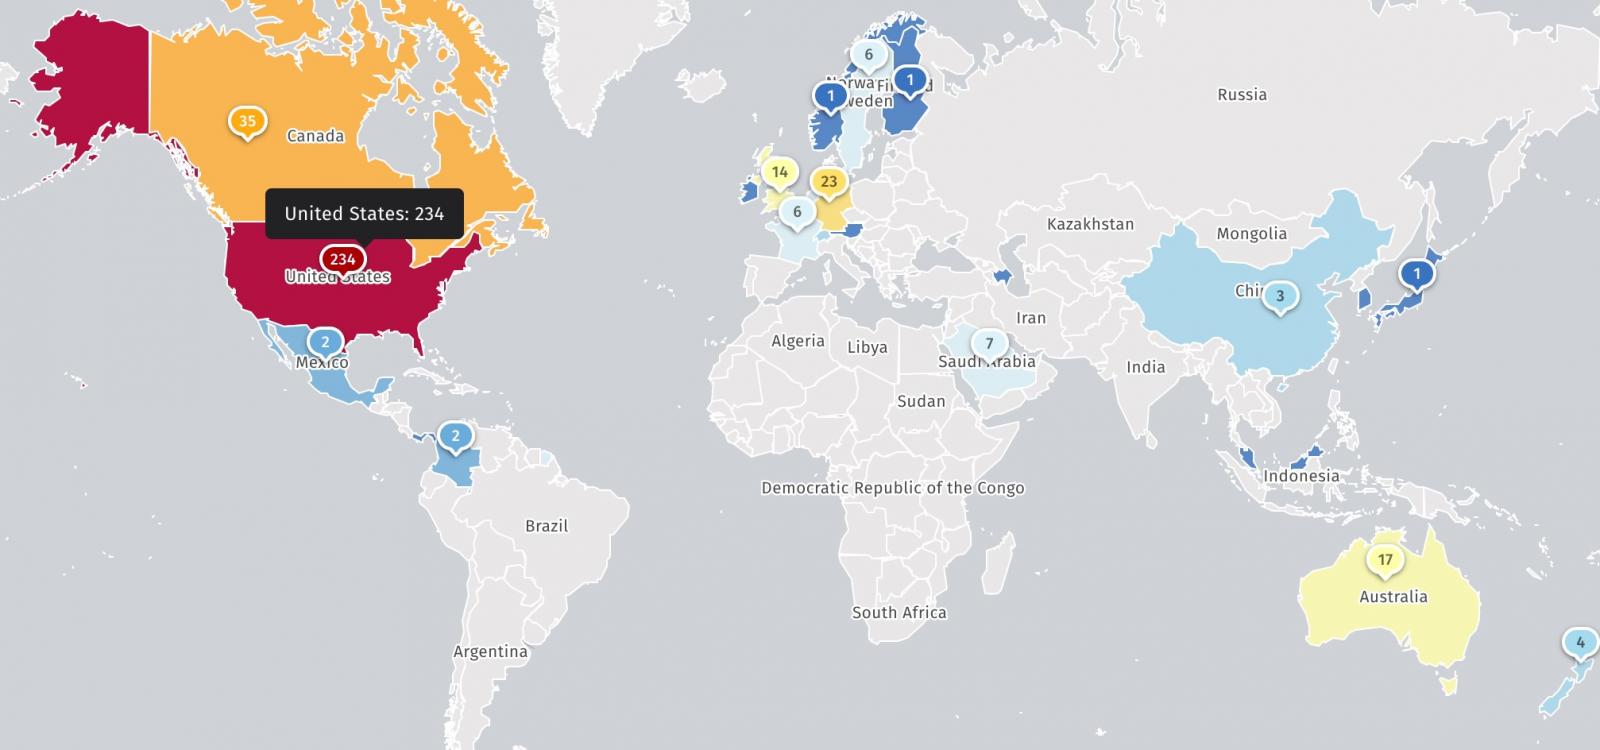
*Internet-exposed Kiteworks instances (Shadowserver)*
File-sharing platforms are frequently targeted by cybercrime groups for data theft and extortion due to the sensitive nature of the documents they store.
A notable example is the **Clop** extortion gang, which has a history of exploiting vulnerabilities in enterprise file-sharing platforms. **Clop** previously targeted a legacy **Kiteworks File Transfer Appliance (FTA)** software, then under the **Accellion** brand, in zero-day attacks.
At the time, **Accellion** reported that 300 customers used the 20-year-old legacy **FTA** software, with fewer than 100 experiencing breaches and less than two dozen suffering significant data theft.
That **Clop** campaign led to numerous data breaches impacting high-profile entities, including cybersecurity firm **Qualys**, energy giant **Shell**, the **Reserve Bank of New Zealand**, supermarket giant **Kroger**, **Singtel**, the **Australian Securities and Investments Commission (ASIC)**, the **Office of the Washington State Auditor**, and several universities.
In February 2021, **Five Eyes** member nations issued a joint security advisory concerning these attacks and subsequent extortion attempts, urging **Accellion** customers to block internet access to vulnerable servers and apply updates.