Malicious Twitch Browser Extension Exposes 30,000 Users' OAuth Tokens
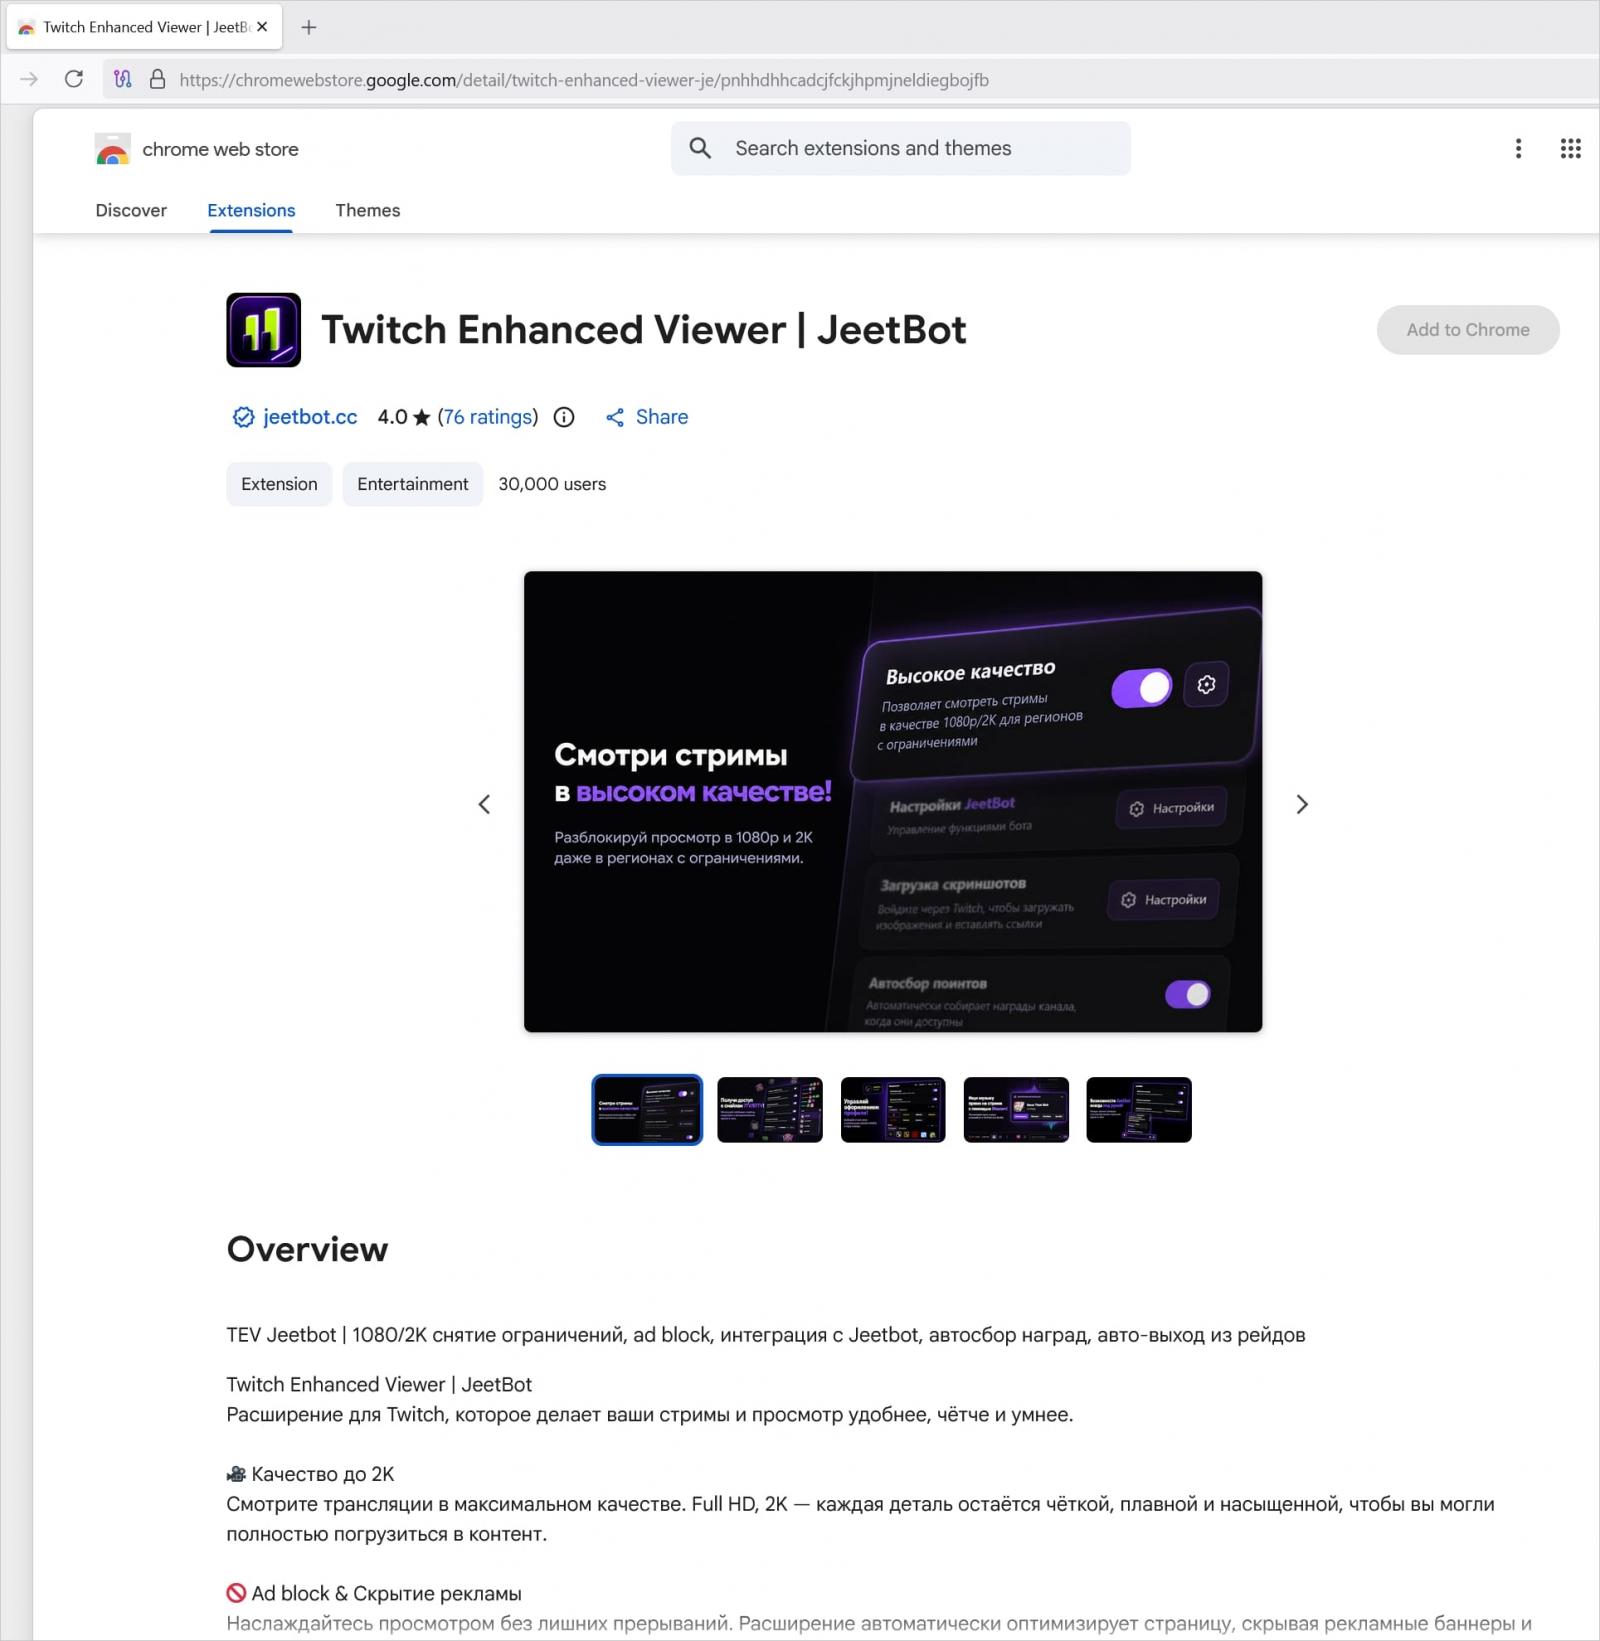
A popular browser extension, "Twitch Enhanced Viewer | JeetBot," with over 30,000 installs, has been found to transmit users' Twitch OAuth session tokens to a commercial bot service. This exposes sensitive authentication credentials, potentially compromising user accounts. The extension, available on official Chrome and Firefox stores, masquerades as a legitimate tool offering ad blocking and region bypass features.

A browser extension named **Twitch Enhanced Viewer | JeetBot**, widely available in the official **Chrome** and **Firefox** stores, has been found to siphon users' **Twitch** OAuth session tokens.
With over 30,000 installations, the extension promotes itself as a legitimate third-party utility for **Twitch**, promising features like ad blocking, forced 1080p playback, region restriction bypass, and automated channel-point collection.
### How the Token Theft Occurs
An analysis conducted by application security company **Socket** revealed that the extension intercepts the authorization header used by the **Twitch** web client. It then extracts the user's OAuth token and transmits these credentials through proxy servers.
These servers are operated by **JeetBot**, a commercial Russian-language streaming and chatbot service that provides tools for **Twitch**, **Kick**, and **VK Live**.
In current versions of the extension, the token is directly appended to redirected proxy requests as an `auth=` URL parameter. This crucial detail means the token is logged in cleartext on the proxy server's request logs, making it easily accessible to the software vendor.
"When the extension redirects Twitch’s video playlist request (to `usher.ttvnw[.]net`) through that proxy, it appends the token as an `&auth=` query parameter," **Socket** stated. "Because the token is placed in the URL query string, it is written in cleartext into the proxy server’s request logs."
This process is executed for every **Twitch** channel a user watches, with the exception of ten specific Russian-language channels hardcoded into the extension's codebase.
### Evolving Deception and Misleading Disclosures
**Socket** researchers noted that earlier iterations of the extension employed more overt credential-theft mechanisms.
Interestingly, the product description in the **Firefox** Add-ons store included a disclaimer regarding a previously used mechanism. It stated, "Previous versions of the extension transmit your OAuth-twitch token to our server. This is necessary for the stream to run in 1080/1440p." (machine translated).
Conversely, the data privacy disclosure for the **Chrome** variant of **Twitch Enhanced Viewer | JeetBot** explicitly claimed that its developer "disclosed that it will not collect or use your data." This declaration covered selling user data, transferring it outside of "core functionality," or using it for "creditworthiness or for lending purposes" – claims that appear to be directly contradicted by **Socket's** findings.
As of the time of publishing, the extension remains available on both the **Chrome** Web Store and the **Firefox** Add-Ons store.
### Recommendations for Users and Developers
**Socket** researchers strongly advise users to remove the extension from their browsers immediately. Furthermore, they recommend disconnecting all active sessions within **Twitch** and then re-authenticating to invalidate any tokens that may have been compromised and forwarded.
Developers are urged to exercise caution and avoid routing requests containing authentication headers or tokens through unverified third-party servers.