Microsoft Bolsters Entra ID Security Against Script Injection Attacks
Microsoft is rolling out enhanced Content Security Policy (CSP) defenses for **Entra ID** sign-ins, aiming to block external script injection attacks. This proactive measure, part of the **Secure Future Initiative (SFI)**, will restrict scripts to trusted Microsoft CDN domains, significantly reducing the risk of cross-site scripting (XSS) and credential theft.

**Microsoft** has reminded its customers about upcoming security enhancements for the **Entra ID** authentication system, specifically targeting protection against external script injection attacks. These changes, initially announced in November 2025, are set to begin enforcement next month.
### Enforcing Content Security Policy
Starting mid-October 2026, **Microsoft** will progressively enforce additional **Content Security Policy (CSP)** defenses. This policy will strictly limit which scripts can run during **Entra ID** sign-ins, allowing only those originating from trusted **Microsoft** content delivery network (CDN) domains. The full rollout is expected to conclude by late October 2026, at which point all users will benefit from enhanced protection against various sign-in security risks.
### Mitigating Cross-Site Scripting (XSS)
This initiative is a critical step in combating cross-site scripting (XSS) attacks, where malicious code is injected into websites to compromise user credentials. **Microsoft** stated, "This change helps protect users from threats such as cross-site scripting (XSS) by allowing only trusted Microsoft-hosted scripts to run during authentication and blocking unauthorized or externally injected code."
### Recommendations for Enterprise Customers
Enterprise customers are advised to review and cease the use of browser extensions or tools that inject code or scripts into sign-in pages before the new **CSP** changes take effect. **Microsoft** urges IT administrators to test their sign-in scenarios to identify and resolve any potential dependency issues with code-injection tools. Admins can monitor for **CSP** violations, which will appear as red text in the browser developer console, providing details about blocked scripts.
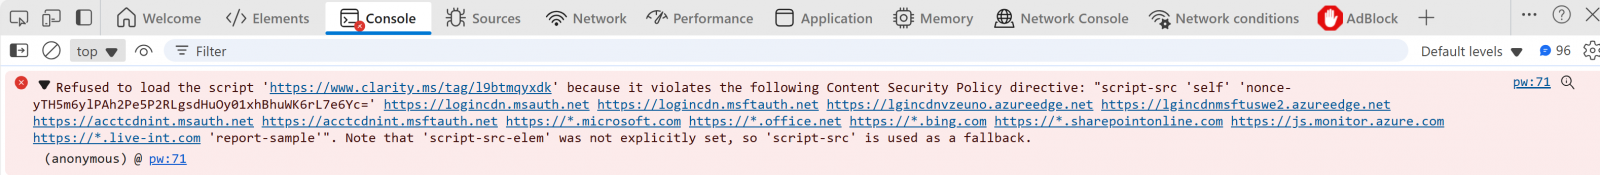
**Microsoft** clarified that users will still be able to sign in even if unsupported script injection tools cease to function. This update is a default service change and does not require tenant configuration. Importantly, **Microsoft Authentication Library (MSAL)** and API-based authentication flows remain unaffected, as **CSP** enforcement applies exclusively to browser-based sign-in experiences via `login.microsoftonline.com`.
### Part of the Secure Future Initiative
These security enhancements are a component of **Microsoft**'s broader **Secure Future Initiative (SFI)**. This initiative was launched following the May and June 2023 breaches where Chinese hackers compromised **Exchange Online** mailboxes belonging to numerous organizations and individuals worldwide.
Under the same initiative, **Microsoft** has also taken steps such as disabling all **ActiveX** controls by default in Windows versions of **Microsoft 365** and **Office 2024** apps, and updating **Microsoft 365** security defaults to block access to Office, SharePoint, and OneDrive files via legacy authentication protocols.