Microsoft's X Account Hijacked in Crypto Pump-and-Dump Scheme
**Microsoft**'s official **X** account, boasting over 13 million followers, was recently compromised in what appears to be a cryptocurrency pump-and-dump scheme. Attackers leveraged the account to promote a dubious '$Clippy' token, leading to an immediate investigation and strong condemnation from the tech giant. This incident highlights a growing trend of high-profile social media account takeovers targeting prominent organizations for financial manipulation.

On Thursday, unknown attackers gained unauthorized access to **Microsoft**'s official **X** account (@Microsoft), which commands over 13 million followers. The compromise was swiftly exploited to promote a cryptocurrency token in what security experts are identifying as a pump-and-dump scheme.
### The Attack Vector
The incident began when the legitimate **Microsoft** account followed and reposted content from another **X** account, @clippymsftcto, which was impersonating **Microsoft**'s iconic virtual assistant, **Clippy**. While @clippymsftcto has since been suspended, another account, @ClippyMSFT, continued to promote a '$Clippy' crypto token, falsely claiming a direct liquidity pool with '$MSFT' stock.
### Microsoft's Response and Investigation
**Microsoft** promptly removed the unauthorized posts and confirmed the breach, stating: "We have confirmed unauthorized access to our account on **X** including posts that did not come from **Microsoft**... The account has been secured and the unauthorized posts have been removed, and we are continuing to investigate the circumstances."
In a subsequent, now-deleted tweet, **Microsoft** issued an apology and emphasized its non-endorsement of any cryptocurrency or crypto-related token. The company also declared its intent to pursue legal action:
"We are aware of a cryptocurrency token being promoted in connection with $MSFT stock, including the unauthorized use of the Clippy brand and **Microsoft**-related intellectual property. **Microsoft** has not authorized, sponsored, endorsed, or granted permission for the creation, promotion, or use of any cryptocurrency token associated with **Clippy**, **Microsoft**, or $MSFT."
"We are taking this matter seriously and will pursue appropriate legal action to have the unauthorized token and related materials removed. For the avoidance of doubt, **Microsoft** does not endorse or have any affiliation with this token, its creators, or any related cryptocurrency project."
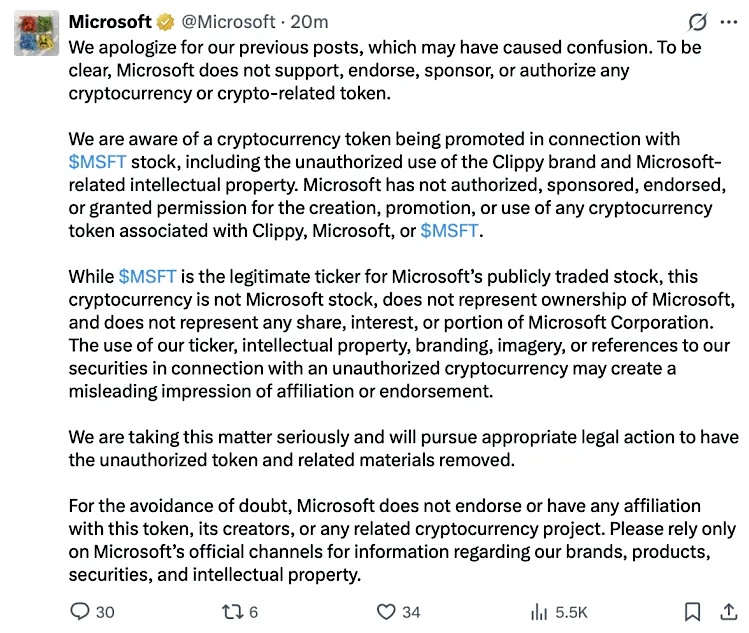
*Microsoft apology post (The Verge)*
### A Pattern of Compromise
This is not an isolated incident for **Microsoft**. In June 2024, the **Microsoft India** **X** account (@MicrosoftIndia), with over 211,000 followers, was similarly hijacked by crypto scammers. In that instance, attackers impersonated **Roaring Kitty** (the handle of notorious meme stock trader **Keith Gill**) to push cryptocurrency wallet drainer malware. They lured followers to a malicious website (presaIe-roaringkitty[.]com) under the guise of buying **GameStop** (**GME**) crypto, ultimately siphoning off crypto assets from unsuspecting victims.
### The Broader Landscape of Social Media Scams
**X** users have been increasingly targeted by a surge of account hijacks and malicious advertisements. Verified organizations frequently fall victim to these tactics, which are often designed to promote cryptocurrency scams and deploy wallet drainers. Blockchain threat analysts at **ScamSniffer** reported in December 2023 that cybercriminals stole approximately $59 million from 63,000 individuals between March and November through a single **Twitter** ad push using the "**MS Drainer**" wallet drainer.
Even government entities are not immune. Last year, the **U.S. Securities and Exchange Commission**'s (**SEC**) @SECGov account was compromised in a **SIM-swapping attack**. The attackers used the account to falsely announce the approval of **Bitcoin** exchange-traded funds (**ETFs**), causing a temporary but significant spike in **Bitcoin** prices. **Eric Council Jr.**, the hacker behind the @SECGov hijack, pleaded guilty in February 2025 and was subsequently sentenced to 14 months in prison for his role in manipulating **Bitcoin**'s value.