New Microsoft Defender Zero-Day 'BigDiskBuster' Blocks Antivirus Updates
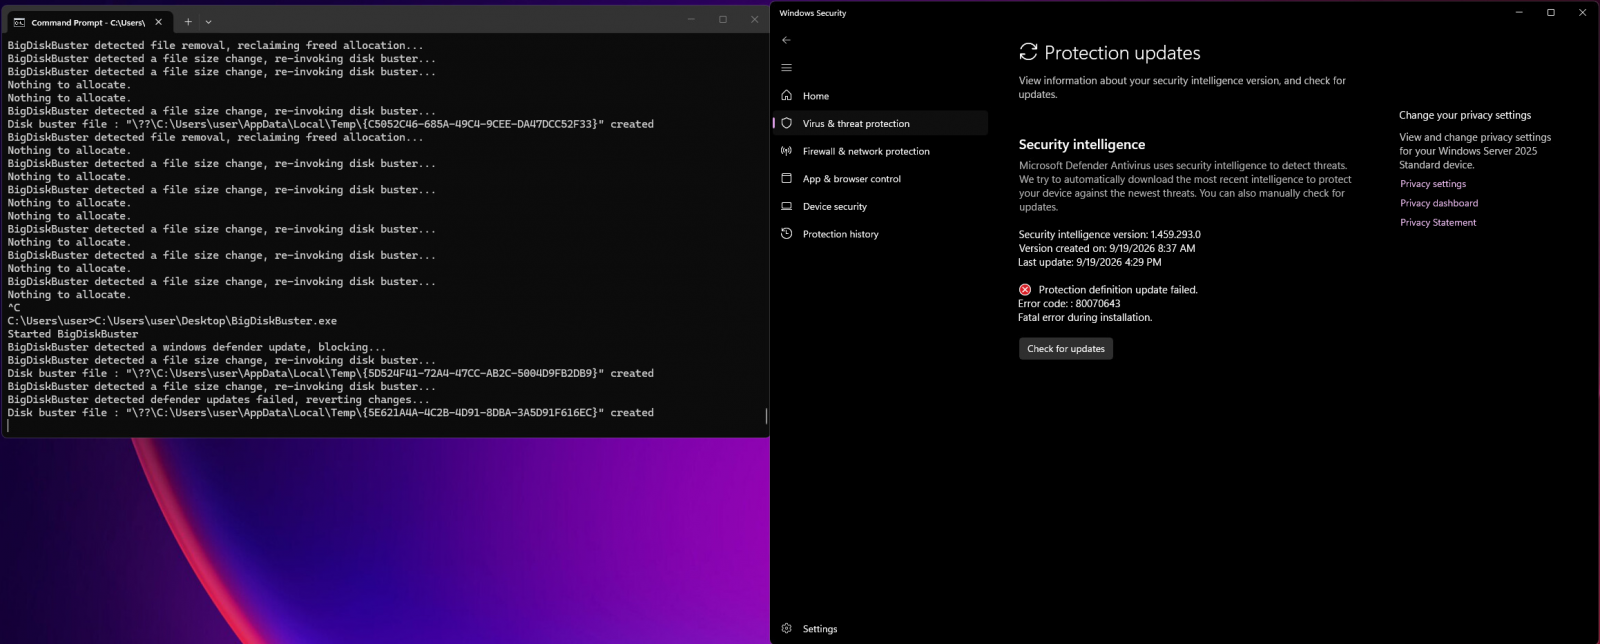
A security researcher, **Abdelhamid Naceri** (also known as **Nightmare Eclipse**), has released another zero-day exploit for **Microsoft Defender**. Dubbed **BigDiskBuster**, this new proof-of-concept tool effectively prevents **Microsoft Defender** from receiving critical definition updates, leaving systems vulnerable to emerging threats.
Over the weekend, security researcher **Abdelhamid Naceri**, known as **Nightmare Eclipse**, disclosed a new zero-day exploit targeting **Microsoft Defender**. The exploit, named **BigDiskBuster**, is designed to block antivirus updates on affected systems.

### BigDiskBuster: A Familiar Threat
**Naceri** states that **BigDiskBuster** shares similarities with **UnDefend**, another **Defender** zero-day exploit he released in April. **UnDefend** allowed standard users to prevent definition updates, and **BigDiskBuster** extends this capability, albeit requiring continuous background execution.
According to **Naceri**, the tool operates across all supported **Windows** versions. "Made a funny tool, completely denies defender from updating so you're stuck with your current version if the tool is running in the background," he explained, adding that while the proof-of-concept is somewhat buggy, the core functionality is clear.
### A History of Disclosures
Since April 2026, **Naceri**, who claims to be a former **Microsoft** employee, has publicly released nearly a dozen zero-day exploits. This series of disclosures is reportedly part of an ongoing dispute with **Microsoft** concerning bug bounty programs.
His recent disclosures include **ShieldCrash**, released just two weeks prior, which grants SYSTEM access and bypasses the **ShieldBreak** flaw (**CVE-2026-69414**) patched by **Microsoft** a week earlier. **ShieldBreak** itself was a bypass for **RoguePlanet**, another **Defender** vulnerability **Naceri** disclosed in June and **Microsoft** patched in July.
Other notable zero-day exploits released by **Naceri** this year include **LegacyHive**, **BlueHammer**, **RedSun**, **YellowKey**, **GreenPlasma**, **MiniPlasma**, and **UnDefend**, targeting various **Microsoft Defender**, **BitLocker**, and **Windows** components.
### Microsoft's Response and Ongoing Vulnerabilities
**Microsoft** initially responded to **Naceri's** disclosures with a statement against "malicious activity causing real harm" to customers, which many in the information security community interpreted as a direct threat to the researcher.
While **Microsoft** has addressed some of the vulnerabilities **Naceri** disclosed, such as **ShieldBreak**, **RoguePlanet**, **YellowKey**, **GreenPlasma**, and **MiniPlasma**, several other security issues he brought to light still await official patches.
At the time of reporting, a **Microsoft** spokesperson was unavailable for comment regarding the **BigDiskBuster** denial-of-service zero-day.