Operation KillSwitch: International Sting Downs KillSec Ransomware, Uncovers Teen Admin
An extensive international law enforcement effort, dubbed "Operation KillSwitch," has successfully dismantled the **KillSec** ransomware operation. The coordinated action led to three arrests, the seizure of servers and a dark web leak site, and the identification of a 16-year-old as the group's alleged administrator. This significant blow to cybercrime highlights the growing complexity and youthful involvement in sophisticated hacking activities.
# Operation KillSwitch: International Sting Downs KillSec Ransomware, Uncovers Teen Admin

An international law enforcement operation dubbed “Operation KillSwitch” has effectively seized the **KillSec** ransomware gang’s data leak site and servers. The action resulted in three arrests and identified a 16-year-old as the group’s alleged administrator.
## Coordinated Global Effort
The coordinated law enforcement action took place on September 30, involving authorities from Belgium, the United States, Finland, Germany, Greece, the Netherlands, Romania, Spain, Switzerland, and the United Kingdom. **Europol** and **Eurojust** also played crucial roles in the investigation, alongside cybersecurity companies **Bitdefender** and **Group-IB**.
According to **Europol**, the action was part of an international investigation led by German authorities, targeting approximately 1,000 suspected attacks worldwide.
## Key Suspects Identified
Investigators identified a 16-year-old as the group’s suspected main operator. Three suspects were provisionally arrested, and eight properties were searched in Greece, Romania, Spain, and the United Kingdom. Authorities also targeted the group’s criminal proceeds.
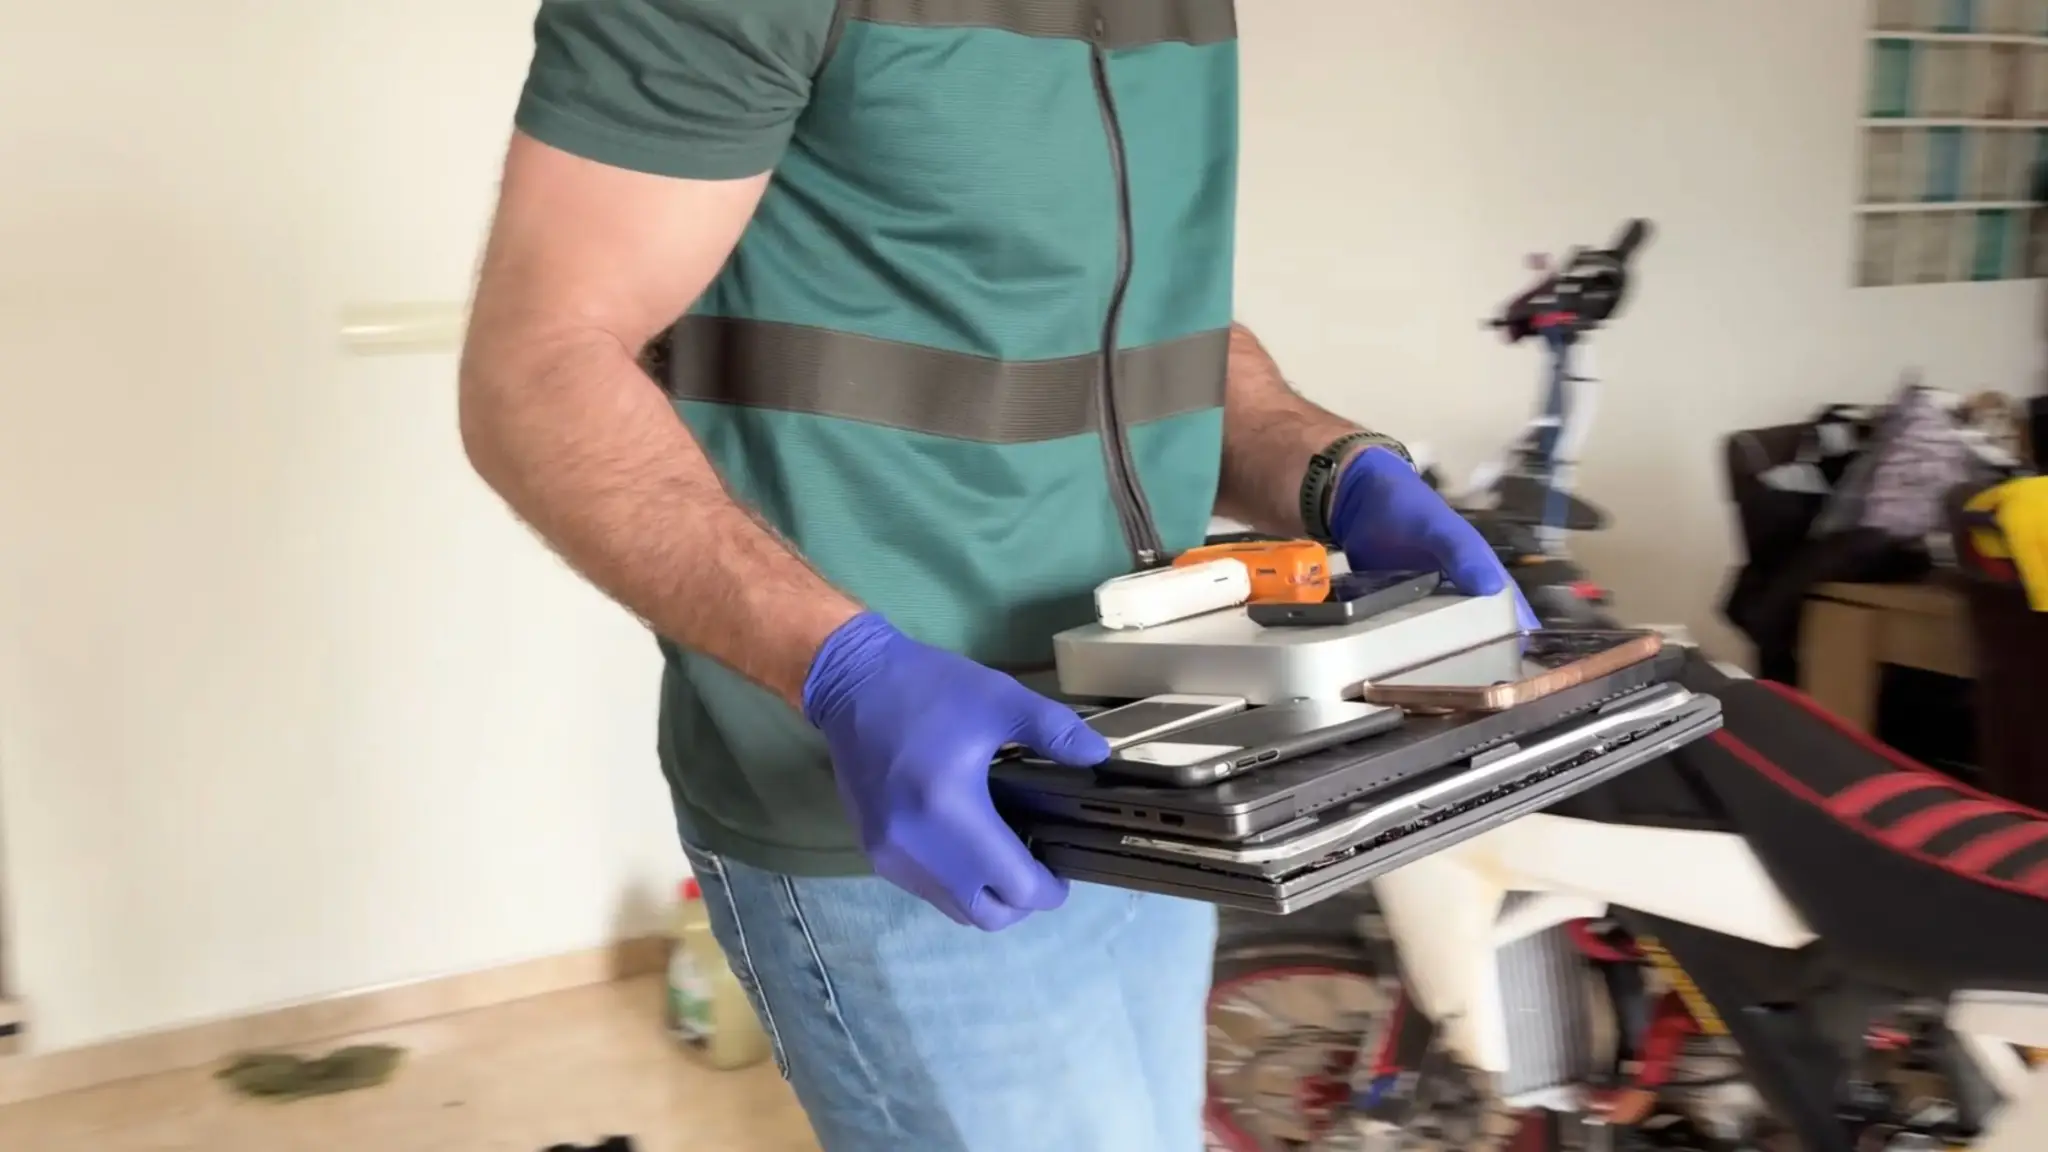
The investigation, which began in 2025, helped law enforcement identify individuals believed to be an administrator, developer, negotiator, and affiliate of the cybercrime group. Another suspected member, described as a developer, turned 18 in August 2026 and was still a minor when some of the alleged crimes were committed.
## Server Infrastructure Dismantled
**Hamburg Police** investigated the group's server infrastructure, leading to the identification and shutdown of five servers, including **KillSec**'s main server and several servers allegedly used to store stolen data.
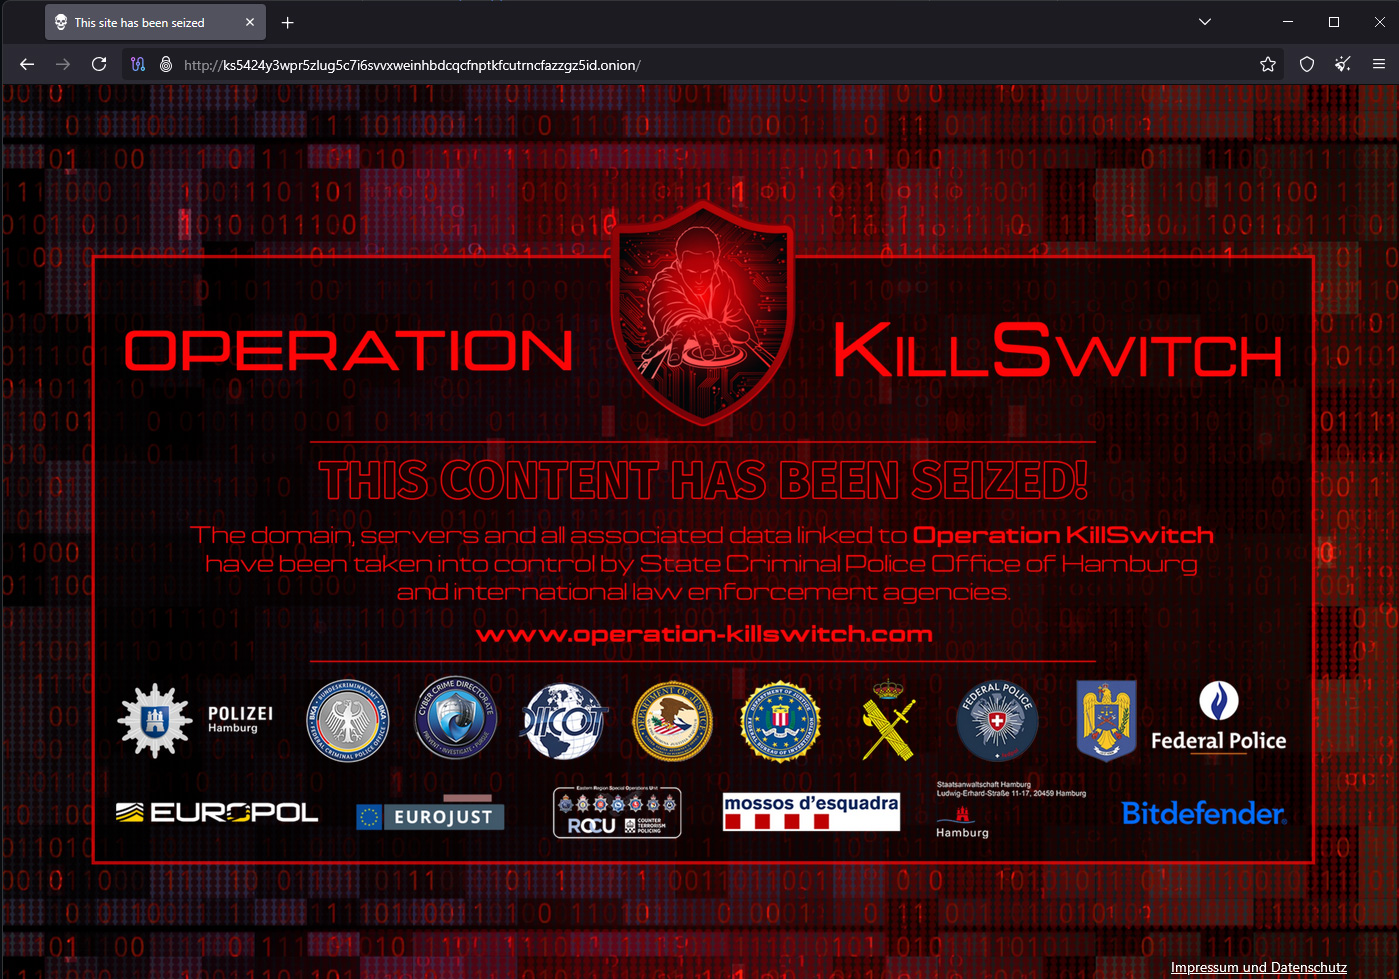
One of the seized sites is **KillSec**'s dark web data leak site, previously hosted at `https://ks5424y3wpr5zlug5c7i6svvxweinhbdcqcfnptkfcutrncfazzgz5id.onion/`, which now displays a seizure message.
### Seizure Banner Message
The seizure banner reads: "The domain, servers and all associated data linked to Operation KillSwitch have been taken into control by State Criminal Police Office of Hamburg and international law enforcement agencies."
Clicking the seizure banner leads to the [Operation KillSwitch](http://www.operation-killswitch.com/) website, which features a law enforcement video detailing the ransomware gang and the arrests.
## Data Seized and Impact Assessed
During the operation, law enforcement also seized at least 110 terabytes of stolen data to prevent continued unauthorized access. This data will be crucial for further analysis and victim identification.
Investigators have so far determined that approximately 500 of **KillSec**’s attacks were successful, though authorities caution that these numbers may change as evidence is further analyzed. At least 70 of the suspected attacks are linked to organizations in Germany, with 18 cases connected to Hamburg.
## KillSec's Modus Operandi
**KillSec** has been active since around 2024, accused of exploiting software vulnerabilities and poorly secured edge devices and platforms to breach corporate systems and steal sensitive data. The threat actors used this stolen data to extort victims via their dark web leak site, threatening publication if a ransom was not paid. **Europol** reports that **KillSec** received "substantial" ransom payments from these data-theft attacks.
Intriguingly, investigators also discovered that members of the group utilized artificial intelligence to help build and maintain their ransomware infrastructure and identify potential victims.
## Ongoing Investigation
Authorities are currently examining seized computers, servers, and other data, while simultaneously attempting to trace **KillSec**'s alleged criminal proceeds, including cryptocurrency. Investigators anticipate that the seized evidence could reveal additional victims, attacks, and individuals involved with the ransomware operation.