Pegasus Spyware Scandal: Polish Probe Reveals Data Exfiltration to Israel, Raising State Security Concerns
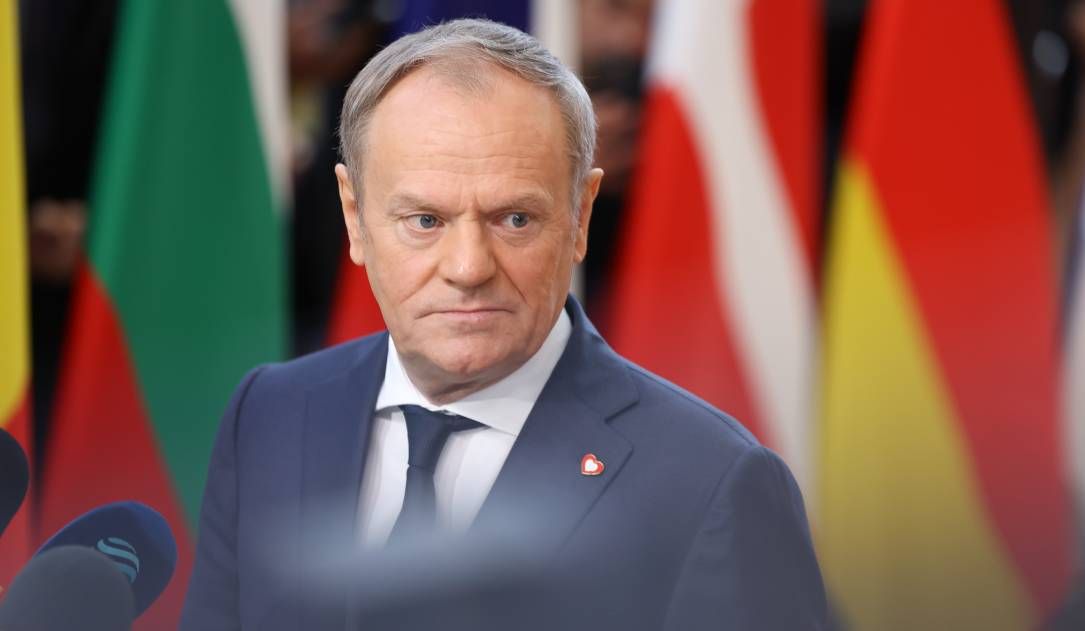
A sprawling investigation in Poland has uncovered evidence that the **Pegasus** spyware, developed by **NSO Group**, harvested data from Polish opposition leaders and other victims, subsequently transmitting it to Israel. Prime Minister **Donald Tusk** has labeled the operation, spearheaded by the country's former ruling party, as one of Poland's most significant scandals since the fall of communism, raising serious questions about national security and the control of sensitive intelligence.
Polish investigators have revealed critical findings in their ongoing probe into the extensive use of **Pegasus** spyware. The investigation points to an alarming scenario where sensitive data collected from Polish citizens, including opposition figures, was transmitted outside the country.
### NSO Group's Unfettered Access
Poland's National Prosecutor’s Office, following an analysis by the Internal Security Agency (**ABW**), stated that the Central Anti-Corruption Bureau (**CBA**) – the entity that ran the spyware program – lacked full control over the **Pegasus** system. Crucially, the server module responsible for infecting mobile devices remained under the exclusive control of **NSO Group**, the Israeli spyware manufacturer.
The **CBA** also reportedly did not possess passwords for many administrative accounts, hindering full verification of the system's functionality, including its data transmission and storage mechanisms. This lack of oversight meant that data collected by the spyware was sent outside of Poland via an anonymizing network using foreign IP addresses, effectively giving **NSO Group** “technical access” to operationally gathered intelligence.
### A "Crime Against the State"
Prime Minister **Donald Tusk**, who initiated the investigation, described the operation as “one of the biggest scandals in Polish history since the fall of communism.” He accused **NSO Group** of collaborating with Israeli intelligence services and highlighted the severity of the situation, stating, “This is no longer [just] a scandal… We’re talking about a crime against the state.”
In February 2024, Tusk's government confirmed that **Pegasus** was used to target a “very long” list of victims, including his own wife and daughter, along with over 500 other individuals. Several former intelligence and security officials are now facing charges for their alleged roles in facilitating these abuses, which were reportedly funded by misusing a government fund intended for crime victims.
### Operational Security Risks for Governments
**John Scott-Railton**, a researcher at **Citizen Lab**, emphasized the critical operational security implications for countries deploying such spyware. Despite **NSO Group**'s longstanding assurances to government clients that it cannot access data collected by **Pegasus**, discovery materials from a 2019 **WhatsApp** lawsuit against the company lend credence to the Polish government’s claims.
Scott-Railton warned that governments using foreign spyware must carefully consider whether their sensitive information, including intelligence on targets and their citizens' data, is being exposed to foreign entities. This incident underscores the inherent risks not only to the value proposition of acquiring foreign spyware but also to the national security of the government wielding it.