Ransomware Gangs Now Exploiting Critical JetBrains TeamCity Flaw
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a stark warning: ransomware gangs are actively exploiting a critical authentication bypass vulnerability in **JetBrains TeamCity** On-Premises. This flaw, identified as **CVE-2026-63077**, allows unauthenticated attackers to execute arbitrary commands, posing a significant risk to CI/CD pipelines and sensitive data.

The **U.S. Cybersecurity and Infrastructure Security Agency (CISA)** has alerted federal agencies that ransomware groups are now leveraging a critical vulnerability in **JetBrains TeamCity**, a popular Continuous Integration and Continuous Deployment (CI/CD) platform.
### The Critical Vulnerability: CVE-2026-63077
**JetBrains** initially patched this security flaw, tracked as **CVE-2026-63077**, on July 25 in **TeamCity On-Premises** versions 2025.11.7 and 2026.1.3. Described as a critical authentication bypass, it enables attackers with HTTP(S) access to execute arbitrary operating system commands.
According to **JetBrains**, an unauthenticated attacker could exploit this vulnerability via the **TeamCity** agent polling protocol. This bypass grants them the ability to execute commands with the privileges of the **TeamCity** server process.
Successful exploitation could lead to the exposure of **TeamCity** data, configurations, and stored credentials. It also risks modifying server state and potentially compromising the integrity of build artifacts and downstream CI/CD pipelines.
### CISA's Warnings and Active Exploitation
Less than two weeks after the patch, on August 5, **CISA** added **CVE-2026-63077** to its **Known Exploited Vulnerabilities Catalog (KEV)**. Federal agencies were subsequently mandated to secure their networks against ongoing attacks within three days.
On August 7, **JetBrains** confirmed active exploitation in the wild, providing indicators of compromise and urging customers unable to patch immediately to restrict access to trusted networks.
### Ransomware Groups Join the Fray
**CISA** recently updated its **KEV** catalog again, specifically flagging **CVE-2026-63077** as being abused by ransomware gangs. This marks a concerning escalation.
Since October 2023, **CISA** has identified four **TeamCity** security issues exploited in the wild, all of which have also been leveraged in ransomware campaigns.
Security threat watchdog **Shadowserver** is currently tracking just over 160 **TeamCity** servers that remain unpatched against the **CVE-2026-63077** flaw. This number is down from an initial count of 700 internet-exposed vulnerable servers identified immediately after the patch release.
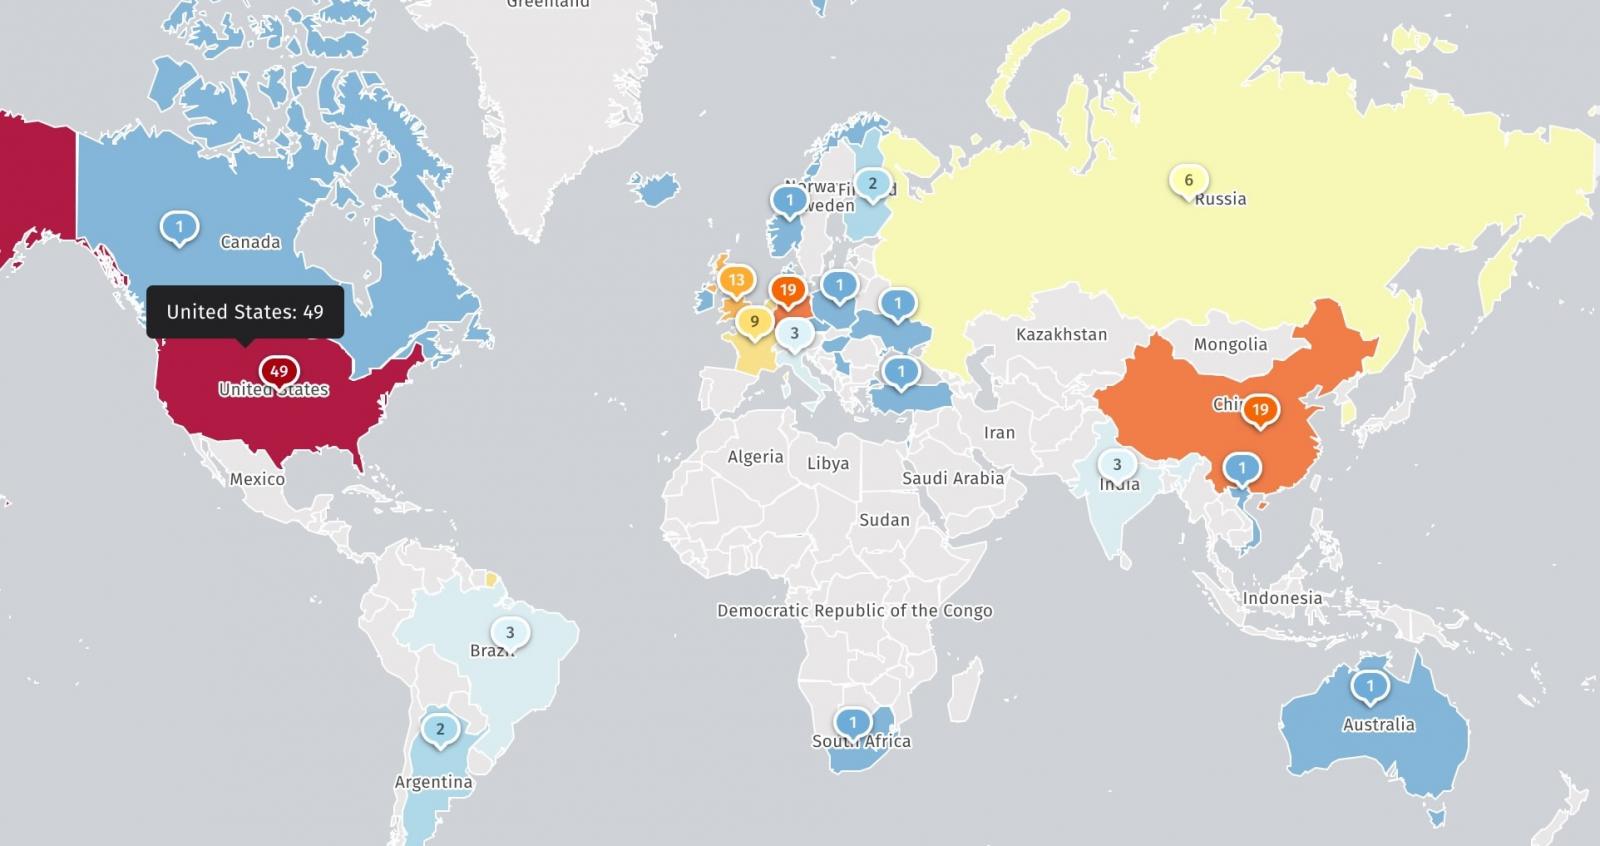
*Unpatched TeamCity servers exposed online (Shadowserver)*
Given the history of both state-backed hacking groups and ransomware gangs leveraging **TeamCity** vulnerabilities, IT administrators are strongly advised to patch all internet-exposed servers without delay.
For instance, in October 2024, U.S. and U.K. cyber agencies warned that **APT29** hackers, linked to Russia's Foreign Intelligence Service (**SVR**), were targeting vulnerable **JetBrains TeamCity** and **Zimbra** servers at a mass scale.
**TeamCity** is critical infrastructure for many organizations, with **JetBrains** stating that over 30,000 DevOps teams, including those at high-profile companies like **Citibank**, **Amazon Games**, **Tesla**, and **Samsung**, utilize the platform.