New 'Rapuncel' Infostealer Leverages Microsoft-Signed Kernel Driver to Evade 145 AV/EDR Products
A sophisticated malware campaign is exploiting SEO-optimized GitHub repositories to impersonate major software brands, distributing an undocumented information stealer named **Rapuncel**. This campaign is particularly concerning as it deploys a **Microsoft**-signed kernel driver capable of disabling 145 antivirus and EDR solutions, posing a significant threat to IT security professionals and privacy-conscious users.
An active malware campaign is employing a stealthy strategy, utilizing SEO-optimized **GitHub** repositories to mimic well-known software companies. The primary objective is to push a previously undocumented information stealer dubbed **Rapuncel**.
Security researchers at **LastPass** and **Delphos Labs** uncovered this campaign, reporting that it impersonates the **LastPass** password manager brand and at least 39 other companies.
Beyond the **Rapuncel** infostealer, the malicious repositories deliver a **Microsoft**-signed kernel driver. This driver possesses the alarming capability to disable 145 antivirus and endpoint detection and response (EDR) products.
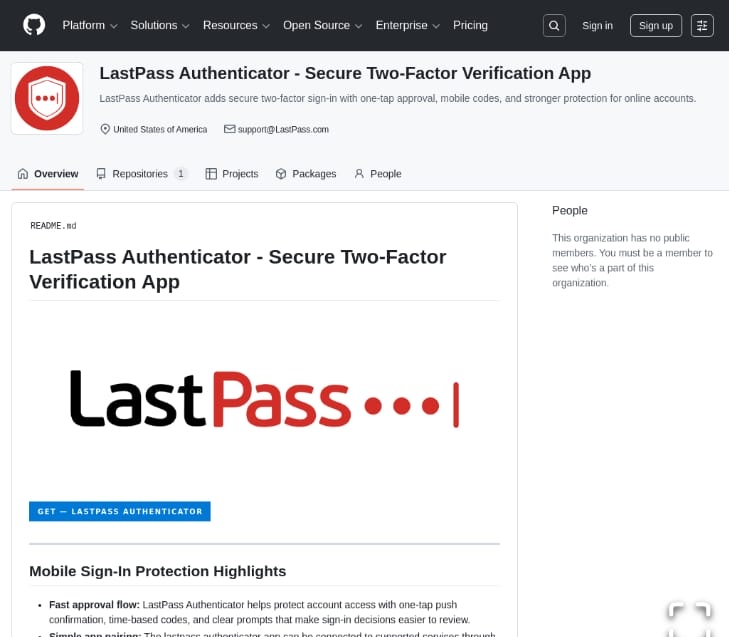
The attack chain typically begins when victims search for popular software, such as **LastPass Authenticator**, and are led to these fake **GitHub** repositories. Clicking download buttons on these fraudulent pages initiates a series of redirections, ultimately leading to payload-delivery servers.
Victims then receive **ZIP** archives, cleverly inflated in size up to 148MB to bypass conventional security scans. Inside these archives, the installer is a copy of the legitimate **Microsoft Visual Studio CoreCLR Debugger**, `vsdbg.exe`, which is renamed and configured to sideload a malicious DLL (`vsdbg.dll`). This installer deploys both the **Rapuncel** infostealer and the `Alinubx.sys` kernel driver, specifically designed to neutralize antivirus software.
The kernel driver is disguised as an **NVIDIA** component named `nvfsflt64.sys` and registers itself as the `NvFsFilter` service.
According to the researchers, this driver functions as an EDR killer, containing a hardcoded list of 145 antivirus and EDR processes it aims to terminate.
"The driver calls `ObOpenObjectByPointer` with `AccessMode=KernelMode`, which bypasses the normal user-mode `SeAccessCheck` path at handle-open time," **LastPass** explains. "It asks the kernel to open the process as kernel code, then kills it. That is why it can defeat Protected Process Light (PPL); the protection many security products rely on to survive an administrator."
Crucially, the driver currently evades **Microsoft**'s vulnerable drivers blocklist. The version used in this campaign is signed through **Microsoft**'s Windows Hardware Compatibility Publisher chain.
While the researchers noted that `Alinubx.sys` contains additional capabilities for file and registry hiding, DLL injection, driver and process interception, traffic manipulation, and port redirection, these features do not appear to be activated in the current campaign.
## The Rapuncel Infostealer
Once security software on a device is terminated, the **Rapuncel** infostealer begins its data exfiltration process. The malware is designed to collect a wide array of sensitive information:
* Credentials stored in 25 web browsers
* Data from 30 cryptocurrency wallets
* **Discord**, **Steam**, and **Telegram** session credentials
* **Windows** Credential Manager contents
* Documents with names containing "password," "seed," "wallet," or "recovery"
* Screenshots from every connected monitor
* Detailed system information
To circumvent **Google**'s app-bound encryption protection present in **Chrome**, **Edge**, and related browsers, **Rapuncel** injects a helper DLL into the application and invokes its own Elevation Service.
The stolen information is then compressed and uploaded to an external endpoint at `2.26.126[.]50` using an **HTTP**-formatted request sent over raw **TCP**.
**Rapuncel** ensures persistence across reboots by establishing itself as a **Windows** service. This means any security tools that reactivate after a reboot are promptly terminated again before the infostealer relaunches.
**LastPass** and **Delphos Labs** have assessed with moderate confidence that **Rapuncel** is a variant of **BoryptGrab**. They also found that its loader was constructed using the **Cruciferra PUROSANGUE** crypter.
Users and organizations are strongly advised to download software exclusively from official websites, exercise extreme caution with dubious **GitHub** repositories, and consider blocking or skipping promoted results on **Google Search** to mitigate risks.