ShinyHunters Breaches Clop Ransomware Site in Escalating Cyber Feud
The notorious extortion group **ShinyHunters** has reportedly breached and defaced the data leak site of the equally infamous **Clop** (also known as **Cl0p**) ransomware operation. This attack, allegedly exploiting an unauthenticated file upload vulnerability, marks a significant escalation in an ongoing feud between the two prominent cybercrime entities, with **ShinyHunters** claiming to have stolen critical server data and **Clop**'s onion service private keys.


In an unusual turn of events within the cyber underworld, the **ShinyHunters** extortion gang has successfully breached the **Clop** ransomware operation's data leak site. The attack involved defacing the **Tor** site and, according to **ShinyHunters**, the theft of server data and the private keys for **Clop**'s onion service.
### Initial Compromise and Defacement
The attack commenced on a Friday night, with **ShinyHunters** claiming to have exploited an unauthenticated file upload vulnerability within **Grav CMS**, the content management system used by **Clop**. This vulnerability allowed them to upload a small text file to **Clop**'s site.
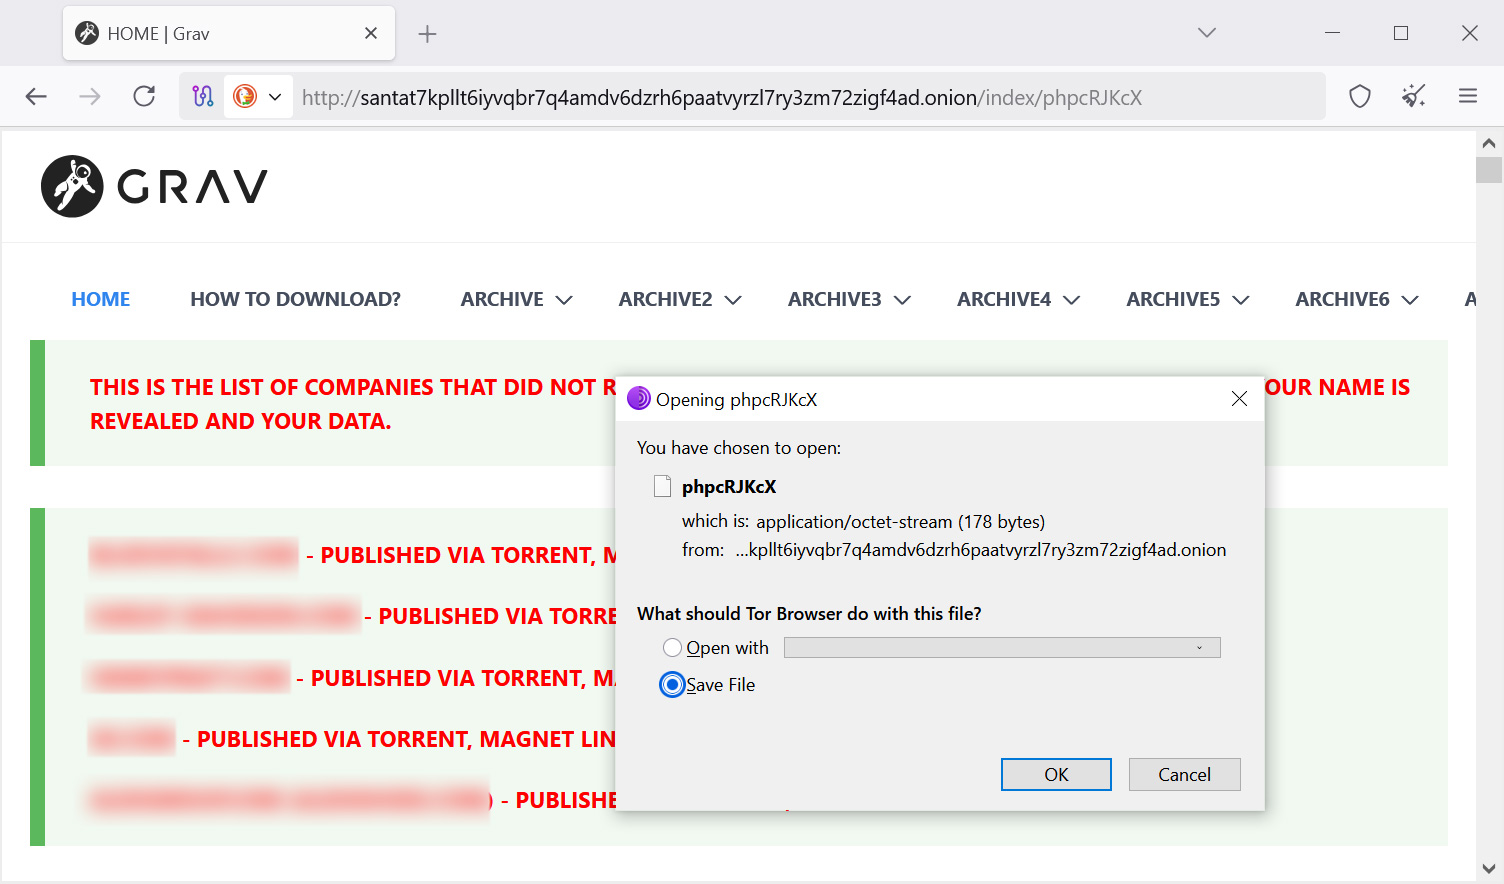
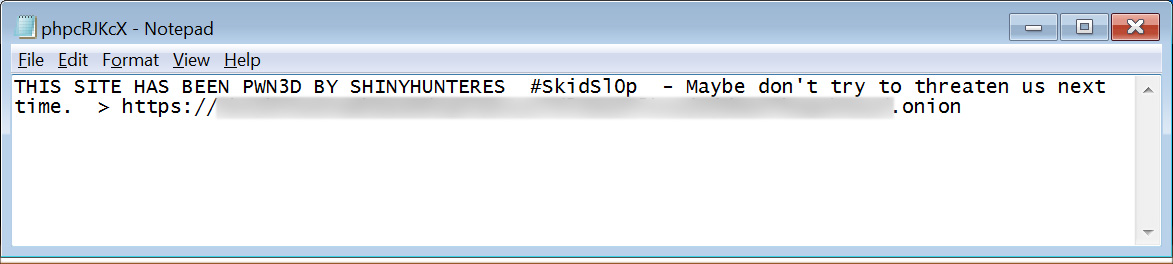
The uploaded file contained a direct message from **ShinyHunters** to the **Clop** ransomware gang, warning against future threats and providing a link to **ShinyHunters**' own data leak site. The message read: "THIS SITE HAS BEEN PWN3D BY SHINYHUNTERES #Skids10p - Maybe don't try to threaten us next time."
Hours later, **ShinyHunters** confirmed they had "completely defaced" the **Clop** site. Visiting the site now reveals a page displaying ASCII art of Umbreon, a **Pokémon** that serves as **ShinyHunters**' logo, accompanied by the message, "rooting your systems since '19 ;)" and another link to their **Tor** site.
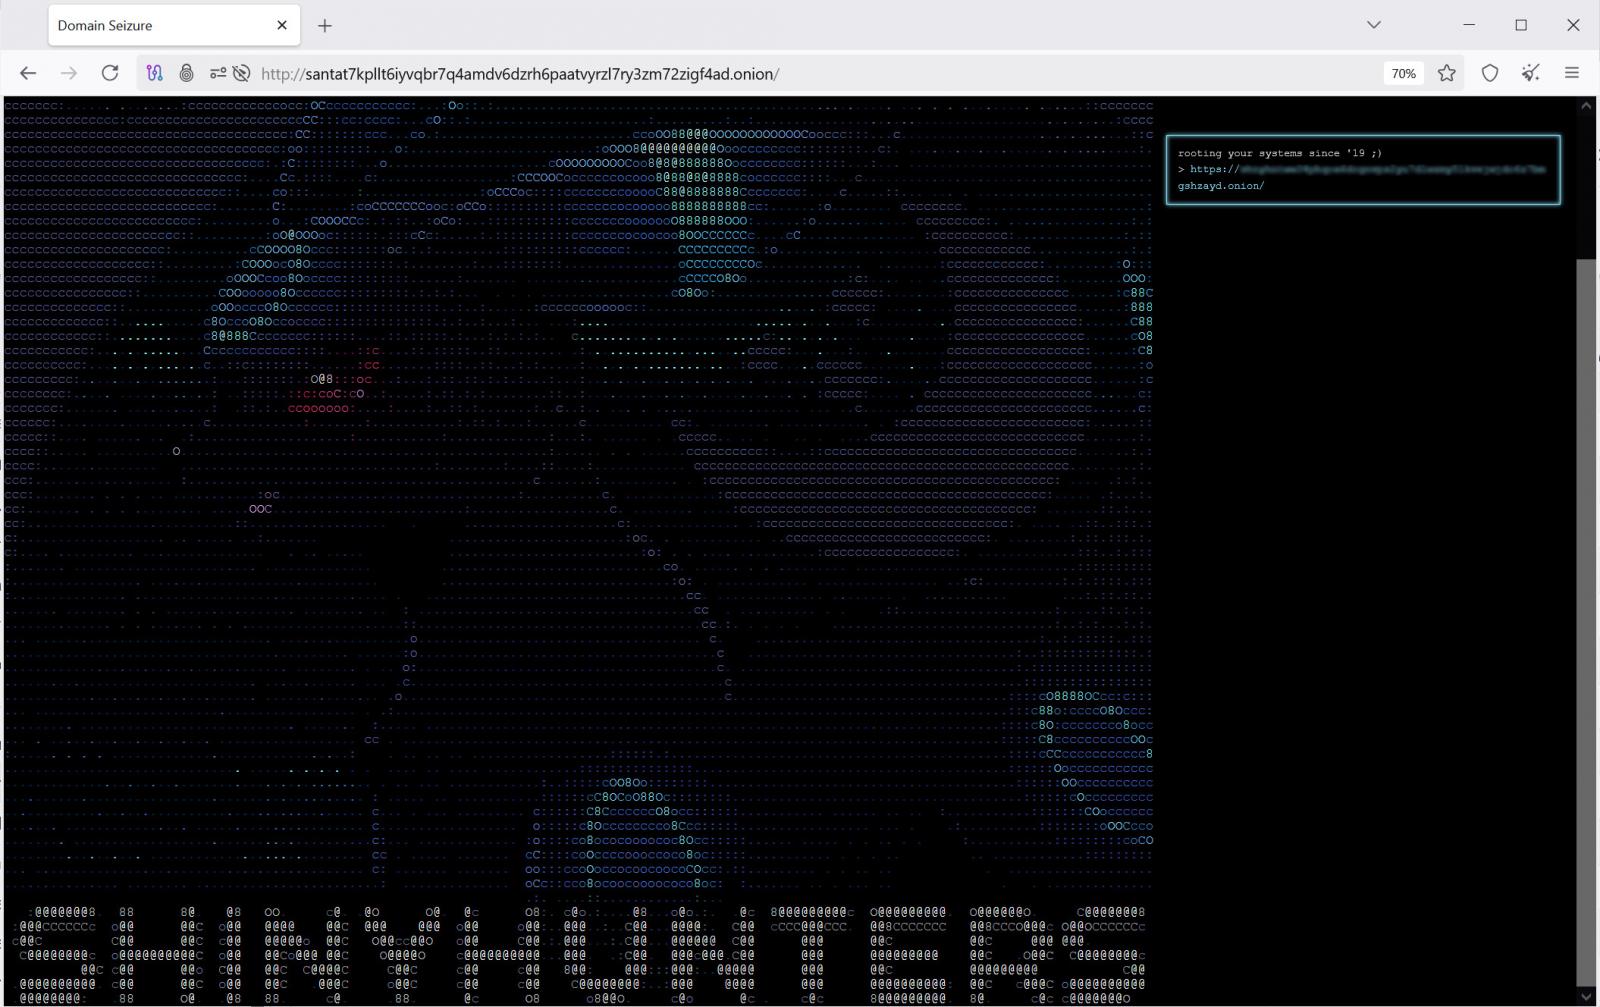
As of this report, the defaced page remains active on **Clop**'s infrastructure.
### Claims of Data Theft and Control
**ShinyHunters** asserts that they gained "full access" to the **Clop** server, leading to the theft of source code, **Grav CMS** plugins, system logs, and other sensitive data.
"The data we stole includes source codes, gravCMS plugins, and other things. We are still downloading and reviewing them," **ShinyHunters** stated. They also claim to have obtained all files under `/var/log`, which could potentially contain system activity, authentication logs, and IP addresses of visitors.
Perhaps the most significant claim is the alleged acquisition of the private keys for **Clop**'s **Tor** onion service. **ShinyHunters** boasted, "We have their onion keys. So if they kick us out it wouldn't matter at all because we control the private keys to host the same exact onion URL." If validated, this would grant **ShinyHunters** the ability to operate a **Tor** site using **Clop**'s existing onion address on their own servers, effectively hijacking **Clop**'s identity on the dark web.
While the defacement has been independently confirmed, claims regarding the theft of server logs, source code, and **Clop**'s onion private keys have not yet been independently verified. **ShinyHunters** has indicated plans to extort **Clop**, instructing them to make contact within 72 hours via a message on **ShinyHunters**' own leak site.
### A Feud Between Cybercrime Groups
**ShinyHunters** attributes this attack to retaliation for alleged threats made by a **Clop** representative during an ongoing dispute. According to **ShinyHunters**, the feud intensified after they disrupted a **Clop** data theft campaign related to **Oracle E-Business Suite** in October 2025. During this campaign, **Clop** exploited multiple vulnerabilities, including a zero-day flaw tracked as **CVE-2025-61882**, to steal data.
At that time, a group including **ShinyHunters**, calling themselves "Scattered Lapsus$ Hunters," leaked a proof-of-concept exploit that **Oracle** later confirmed matched the one used by **Clop**. **ShinyHunters** then claimed the exploit originally belonged to them and was obtained by **Clop** without authorization.
**ShinyHunters** alleges that tensions escalated, with a **Clop** representative sending a threatening message: "I have more money than you and all of your people combined, I'll kill you soon." These allegations remain unverified, and **Clop** has yet to respond to requests for comment regarding the breach and the claims made by **ShinyHunters**.