ShinyHunters Claims FBI Breach Via Oracle PeopleSoft Zero-Day, FBI Investigates
The notorious **ShinyHunters** extortion group alleges a significant breach of **FBI** systems, claiming to have leveraged a previously unknown zero-day vulnerability in **Oracle PeopleSoft**. The group asserts access to internal services, theft of 2-3TB of sensitive data on employees and job applicants, and subsequent lateral movement into **FBI**-managed **AWS GovCloud** infrastructure. While the **FBI** confirms an investigation into claims of unauthorized activity affecting **FBIjobs.gov**, it has not validated the extent of the breach or data compromise.
The **ShinyHunters** extortion gang has made headlines with claims of a successful intrusion into **FBI** systems. The group asserts that the breach, executed on Monday night, exploited a new, unpatched zero-day vulnerability within **Oracle PeopleSoft**, granting them remote code execution capabilities.
Following initial access, **ShinyHunters** claims to have moved laterally into the **FBI**'s **AWS GovCloud** infrastructure. The alleged haul includes 2TB to 3TB of data, encompassing sensitive information on current and former **FBI** employees, job applicants, and various internal records from services like Criminal Justice, HR, and Medlink.
ShinyHunters also states it is actively exploiting this same alleged zero-day against other organizations, including **Fortune 500** companies.

### FBI Investigates Claims
The **FBI** has acknowledged the claims, issuing a statement: "The **FBI** is aware of claims regarding unauthorized activity affecting **FBIjobs.gov** and is currently investigating." However, the agency has not confirmed the validity of the breach or the alleged data theft.
As evidence of their access, **ShinyHunters** provided a screenshot to BleepingComputer showing the **FBI Jobs** website (**apply.fbijobs.gov**) defaced with the group's signature Umbreon Pokémon logo and a message asserting compromise of employee and applicant data.
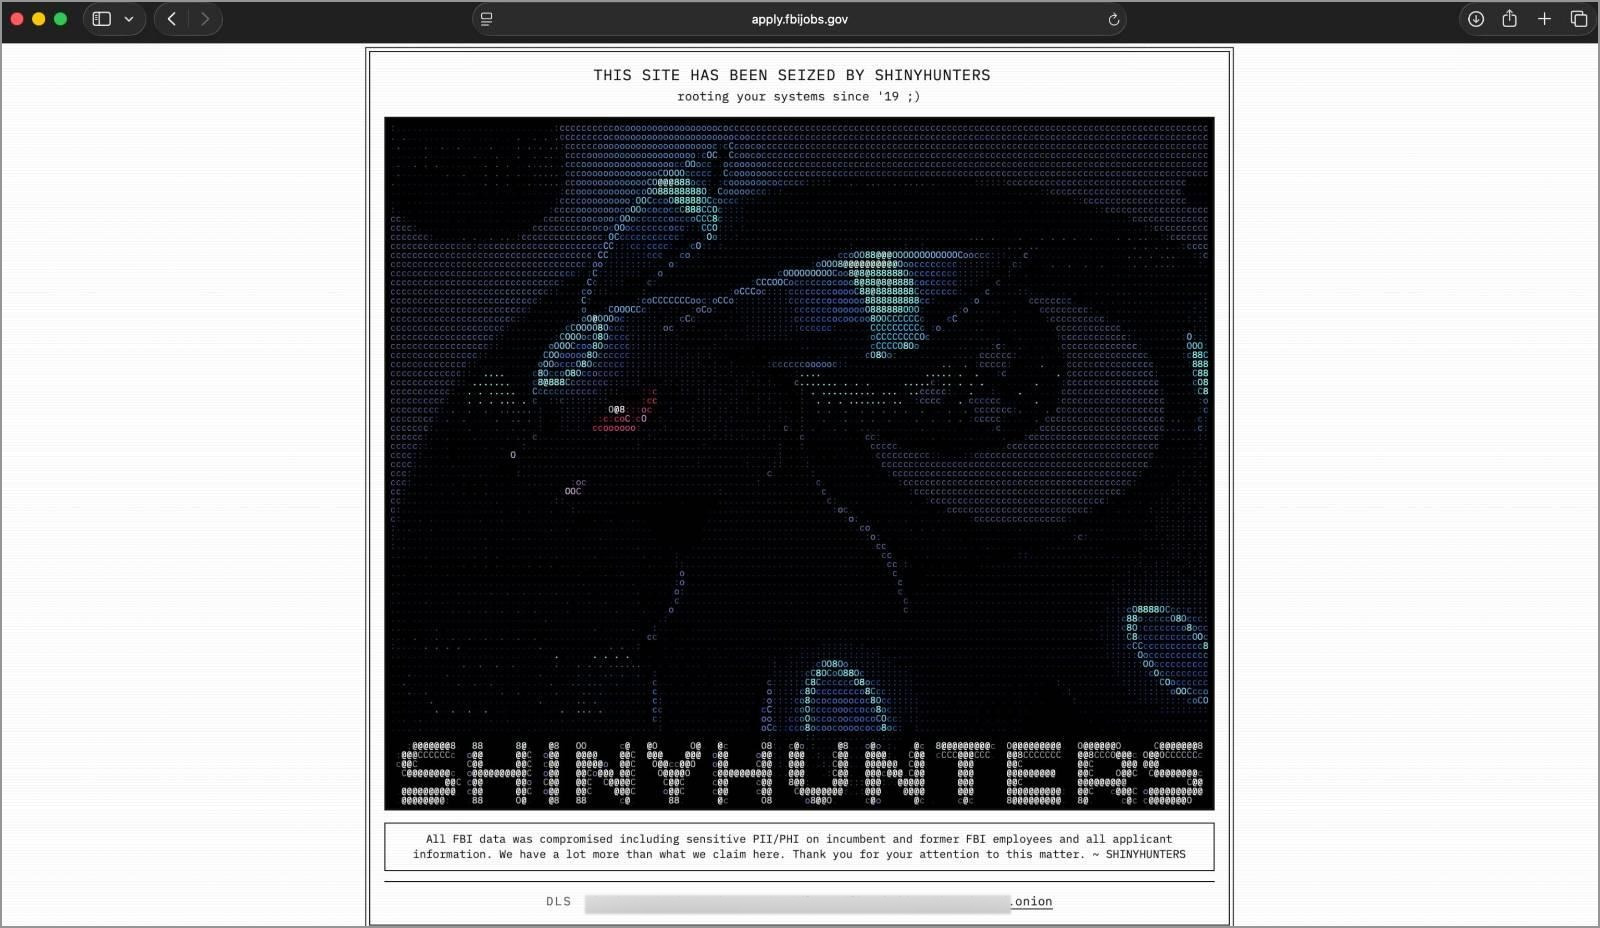
*Allegedly defaced FBI Jobs website
Source: ShinyHunters*
The defacement message explicitly stated, "THIS SITE HAS BEEN SEIZED BY SHINYHUNTERS. rooting your systems since '19 ;)" and claimed the theft of "sensitive PII/PHI on incumbent and former **FBI** employees and all applicant information."
According to **ShinyHunters**, the **FBI** rapidly detected the intrusion, leading to the immediate offline status of affected systems and the display of a maintenance message on the **FBI Jobs** site. The group also reported that access to multiple **FBI** networks was simultaneously terminated following the agency's detection.
### Sample Data and Zero-Day Allegations
**ShinyHunters** shared two sample records, purportedly containing information on **FBI** personnel, including a special agent and **FBI Director Kash Patel**. While these samples were not publicly released, their authenticity and source remain unverified.
**404 Media** initially reported the alleged breach, having received a sample of approximately 5,000 purported **FBI** employee records, some of which were verified for accuracy, including phone numbers linked to **US Department of Justice** personnel.
The core of the intrusion, according to **ShinyHunters**, is a new zero-day in **Oracle PeopleSoft**. The group claims to have found and immediately exploited this vulnerability against the **FBI**, and is now targeting corporations and the **Fortune 500** with the same exploit. Efforts were allegedly made to erase evidence of their activity from compromised servers to obscure the zero-day.
### Retaliation and Prior Incidents
**ShinyHunters** later published a statement on its data leak site, framing the attack as retaliation for an **FBI FLASH** report published in May 2026, which detailed the group's activities. The group disputes claims made in the report regarding exaggeration of access, harassment, swatting, and false claims of compromising material. They also denied being part of "The Com" cybercrime community.
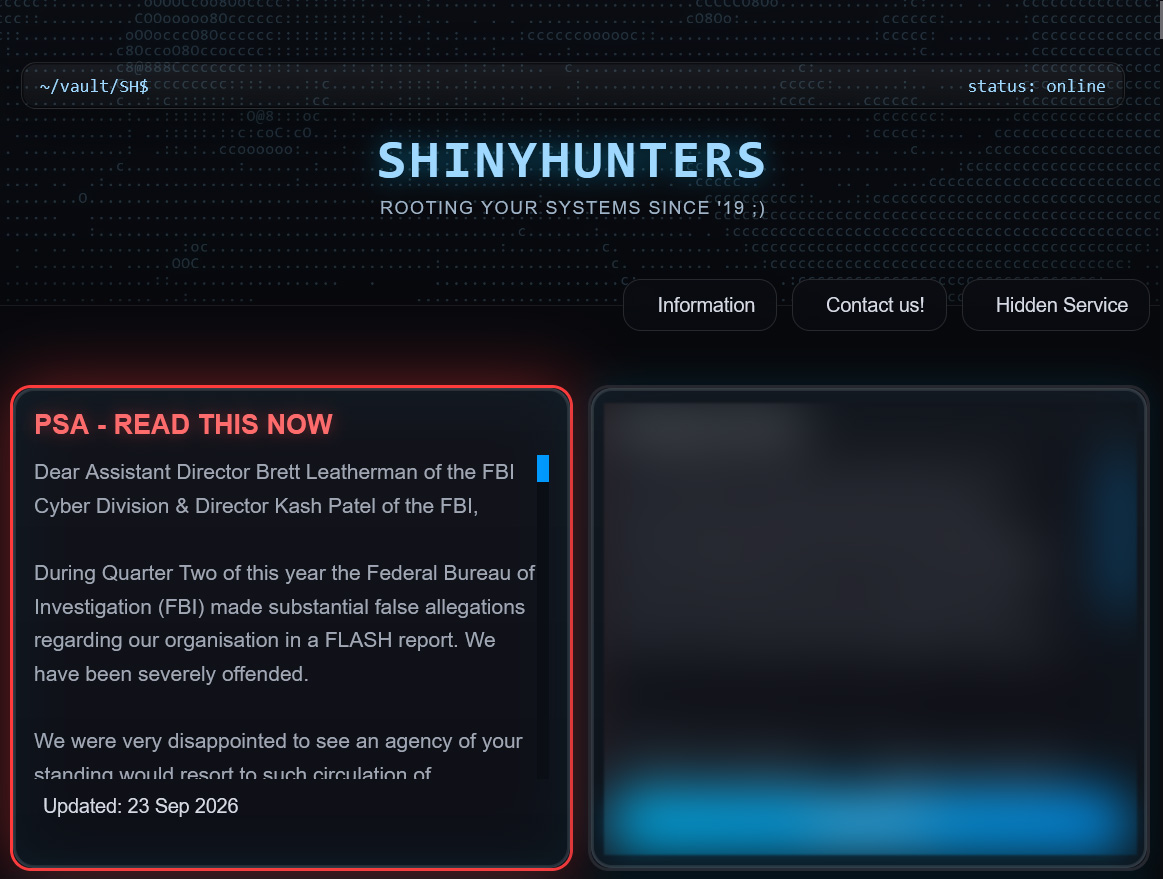
*ShinyHunters statement about FBI attack
Source: BleepingComputer*
**ShinyHunters** issued a one-week ultimatum to the **FBI** to correct or remove the **FLASH** report, asserting that the demand was not financially motivated extortion. When pressed on whether stolen data would be released if the **FBI** did not comply, the group responded with "No comment."
This isn't the first time **ShinyHunters** has been linked to **Oracle** vulnerabilities. The group was previously associated with the leak of a proof-of-concept exploit for an **Oracle E-Business Suite** zero-day, which was later used in **Clop**'s 2025 data theft campaign. **ShinyHunters** claimed ownership of that exploit, alleging **Clop** obtained it without authorization. This dispute recently resurfaced, with **ShinyHunters** breaching and defacing **Clop**'s data leak site, threatening to extort the ransomware operation in retaliation for past threats.