Trezor Investigates Suspected Hardware Wallet Implant from Southeast Asian Reseller
Hardware wallet manufacturer **Trezor** is investigating credible reports of a suspected crypto-theft implant found in a **Trezor Safe 5** device. The device was sold by **CryptoBilis**, a reseller in Southeast Asia, and the incident mirrors a similar supply chain attack impacting **Ledger** wallets earlier this month. Users who purchased devices from **CryptoBilis** are urged to take immediate precautions.

## Supply Chain Attack Raises Alarms for Trezor Users
**Trezor**, a prominent maker of hardware wallets for cryptocurrency, has issued a warning to its users following reports of a potential hardware implant in a **Trezor Safe 5** device. The incident highlights a concerning trend in supply chain attacks targeting critical cryptocurrency infrastructure.
The report originated from an Indonesian user who acquired the **Safe 5** from **CryptoBilis** via **Tokopedia** in August 2026. Upon opening the device, the user discovered an additional circuit board nestled between the main board and the screen, complete with a cellular module and antenna.

### The Nature of the Implant
While **Trezor** has not yet physically examined the device, preliminary information suggests the implant is designed to capture sensitive data. It appears capable of reading information displayed on the screen, including the crucial wallet recovery phrase, and transmitting it over a mobile network when the device is connected.
This sophisticated attack vector could allow threat actors to exfiltrate recovery phrases, granting them full control over a user's digital assets.
### A Troubling Pattern: CryptoBilis Implicated Again
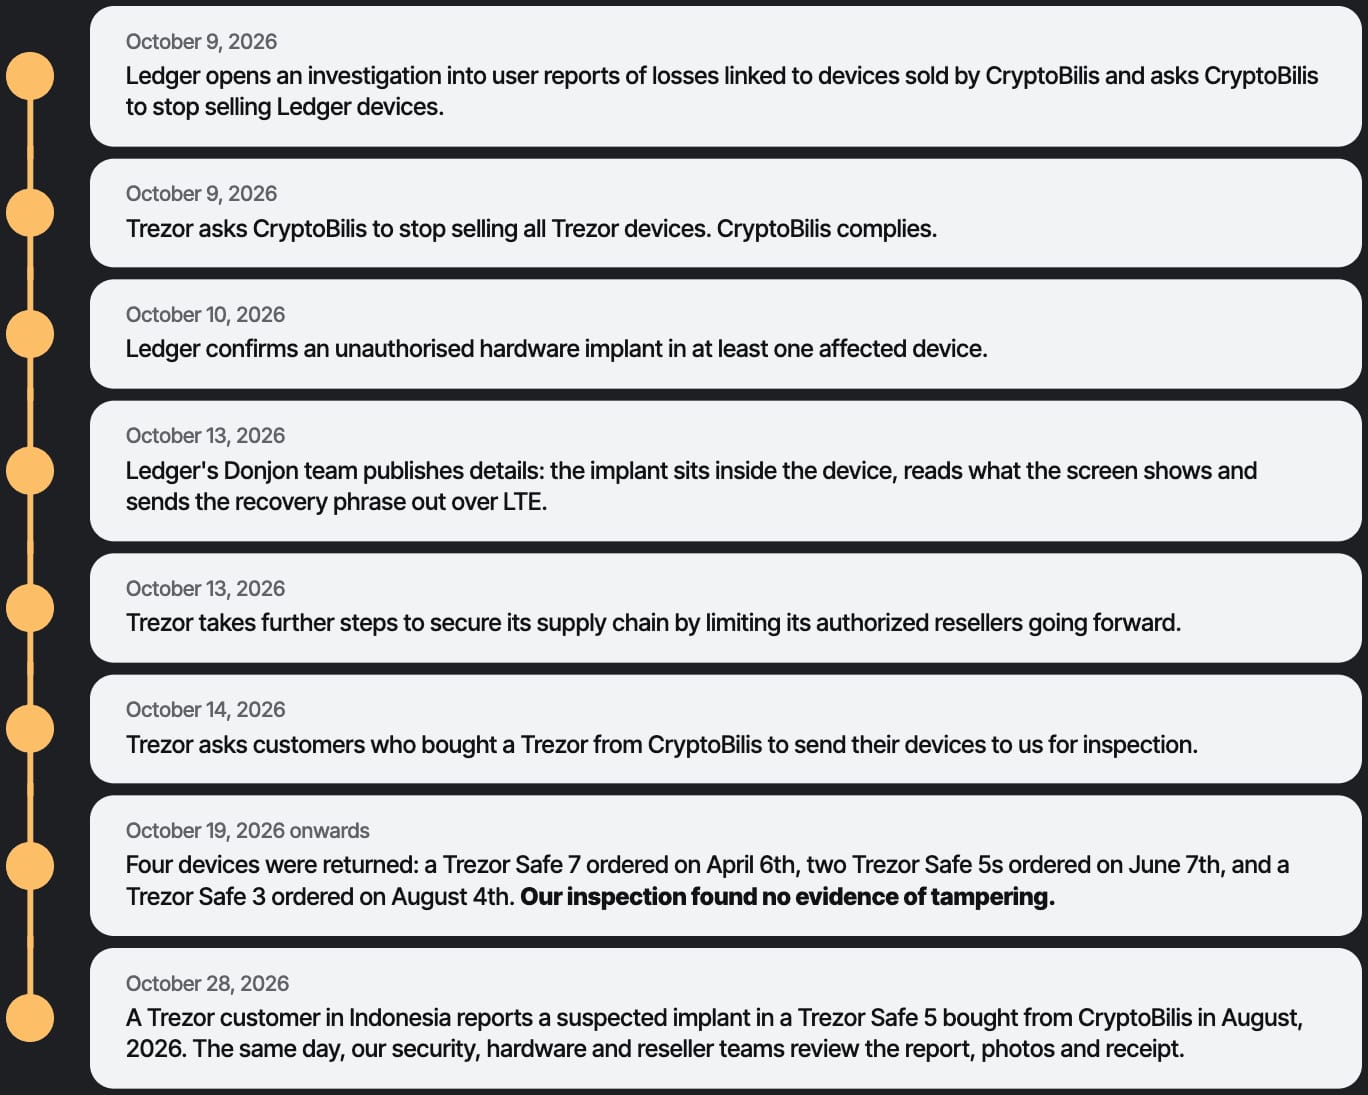
This incident is particularly alarming as **CryptoBilis** was previously implicated in a similar hardware implant compromise affecting **Ledger** wallets earlier in October. The implants in both **Trezor** and **Ledger** devices reportedly share similar form and function, suggesting a coordinated attack or a common threat actor.
Following the **Ledger** incident, **Trezor** proactively ceased sales through **CryptoBilis** on October 9, 2026. The company also announced plans to restructure and tighten its global reseller network to enhance security protocols. **Ledger**, in its response, urged resellers in Southeast Asia and Hong Kong to halt all sales until their investigation concluded.
### Current Status and User Recommendations
**Trezor** has stated it is currently unaware of any funds being stolen as a direct result of this specific supply-chain attack. The company is awaiting the suspected tampered device for a thorough examination and has pledged to provide updates as its investigation progresses.
Meanwhile, the impact of these supply chain attacks is becoming clearer. Multiple reports of losses from **Ledger** users have surfaced, with a recent advisory from the Singapore police adding another $3,500,000 to the tally of stolen funds.
*Source: Trezor*
**Trezor** strongly advises users who purchased any device from **CryptoBilis** from March 2026 onwards to refrain from setting up or using them. For those who have already done so, the recommendation is to immediately move all funds to a newly created wallet with a new, securely generated recovery phrase.
Users with proof of purchase from **CryptoBilis** are encouraged to contact **Trezor** for a replacement device or a voucher for a new one. **Trezor** also cautioned that simply weighing devices is not a reliable method to detect tampering, as these implants can be cleverly concealed.