Volt Typhoon's 'Silent Train' Framework Leverages Zero-Days and Disposable Infrastructure
The Chinese state-sponsored hacking group **Volt Typhoon** has been observed utilizing a sophisticated operational framework dubbed 'Silent Train.' This framework employs rotating chains of compromised devices, including the exploitation of at least four zero-day vulnerabilities, to target high-value systems across critical infrastructure sectors.

**Volt Typhoon**, a persistent threat actor linked to the Chinese state, has been operating a highly elusive framework known as 'Silent Train.' This sophisticated approach involves the on-demand compromise of connected devices, primarily to facilitate zero-day attacks against sensitive targets.
### The 'Silent Train' Modus Operandi
Named for its stealth and ephemeral nature, 'Silent Train' is characterized by its use against specific targets, thorough cleanup after each operation, and continuous refresh of its infrastructure. Researchers at **Black Lotus Labs**, the threat intelligence division of **Lumen**, have been tracking this framework for three years.
Their investigations confirm that **Volt Typhoon** has exploited at least four zero-day vulnerabilities within this framework, primarily targeting edge and management infrastructure across a broad spectrum of industries.
### High-Value Targets and Strategic Focus
The list of targeted entities is extensive, encompassing telecommunication firms, government agencies, defense contractors, educational institutions, utilities/critical infrastructure, satellite service providers, IT firms, Managed Service Providers (MSPs), transportation, aviation, and emergency services.
**Black Lotus Labs** observations pinpoint California, Texas, and Hawaii as the most frequently targeted regions, suggesting a strategic focus aligned with Indo-Pacific geopolitical interests.
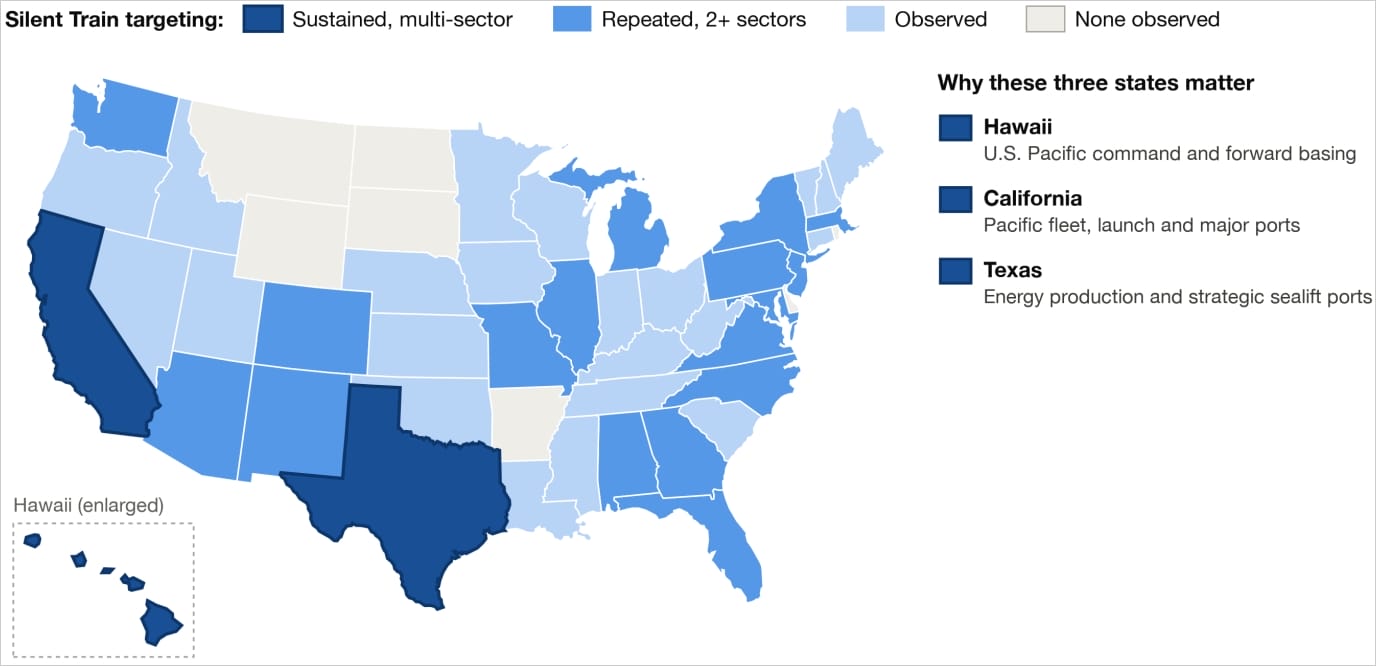
*Source: Black Lotus Labs*
Previously, **Volt Typhoon** gained notoriety for targeting U.S. critical infrastructure, including communications, energy, transportation, and water systems. The **CISA** has warned that the group aims to establish persistent access for potential disruption during future crises or conflicts.
According to researchers, the deployment of 'Silent Train' was partly accelerated following the **FBI**'s disruption of **KV-Botnet**, a previous botnet used by **Volt Typhoon** to mask its activities against U.S. critical infrastructure.
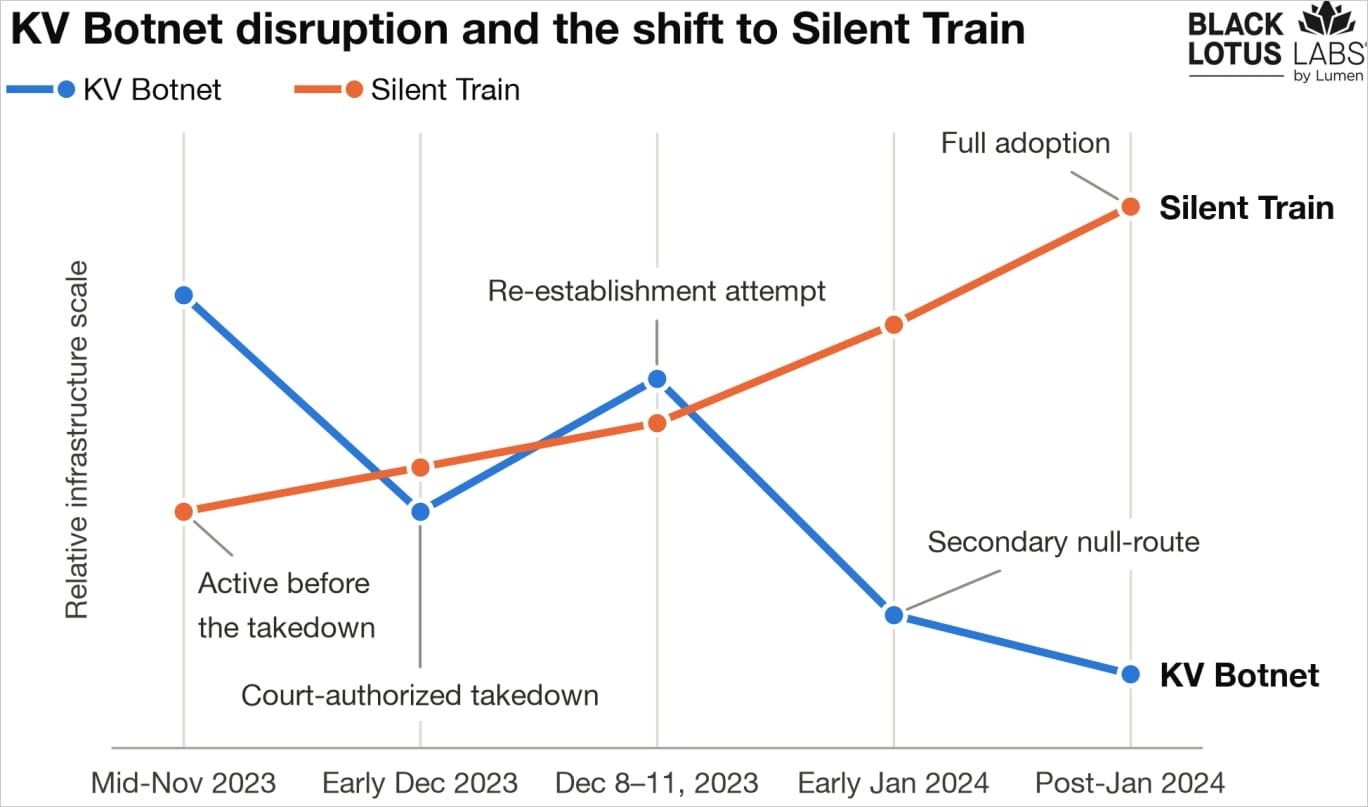
*Source: Black Lotus Labs*
### The Silent Train Relay Network
At its core, 'Silent Train' functions as a relay infrastructure composed of compromised devices, allowing **Volt Typhoon** to obscure the true origin of its attacks. Operators typically route their activities through Virtual Private Server (VPS) infrastructure outside the United States, then pivot through hacked devices like routers that serve as intermediate relays before launching their final assaults.
**Black Lotus Labs** reports that **Intelbras** modems have been used as overseas relays, while **Netgear Orbi** devices have acted as hops within the U.S.
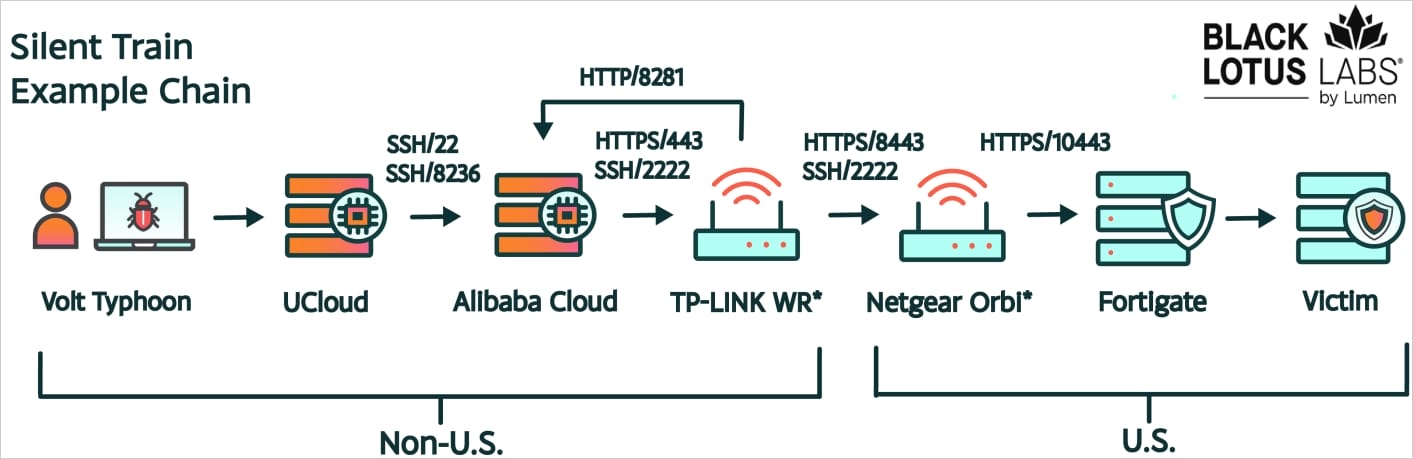
*Source: Black Lotus Labs*
This operational framework facilitates vulnerability exploitation, credential theft, data exfiltration, and the maintenance of persistent remote access to compromised systems.
### Zero-Day Exploitations Uncovered
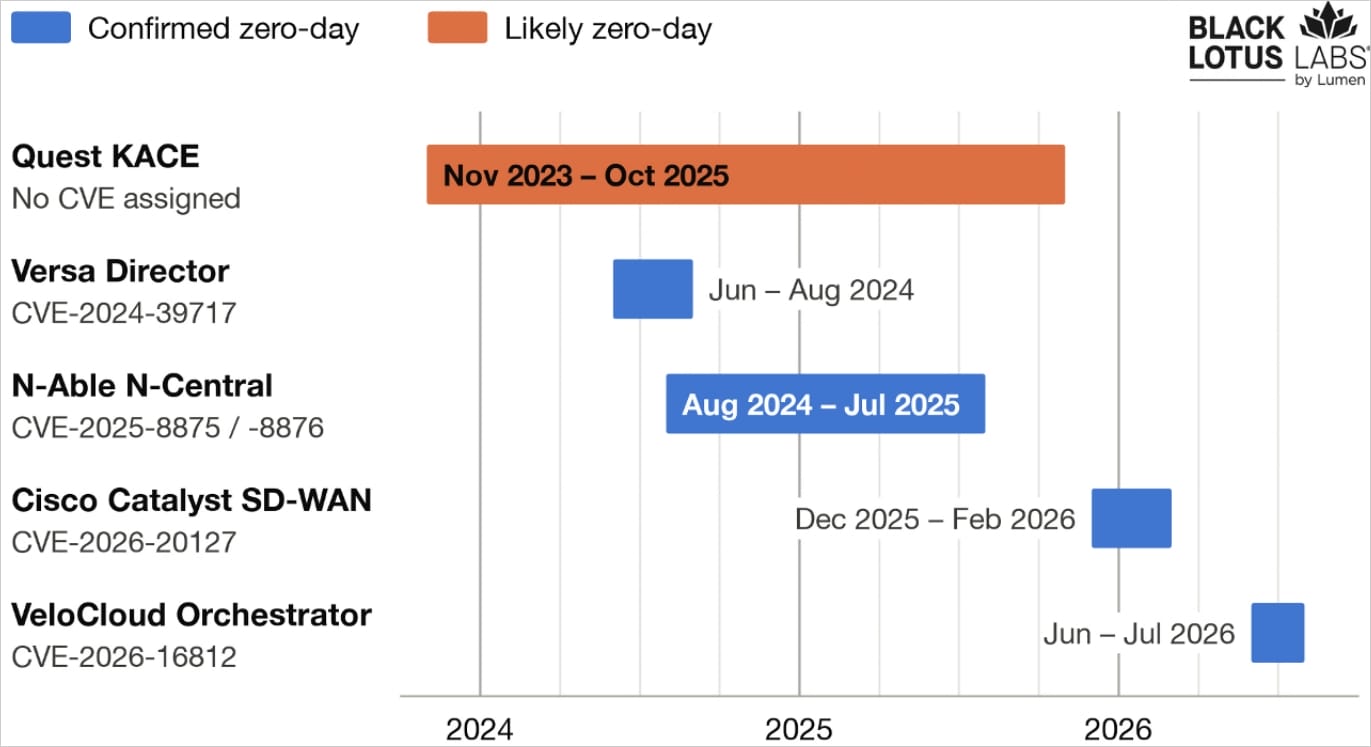
Through meticulous monitoring of 'Silent Train' activity, researchers have identified the exploitation of several zero-day vulnerabilities in the following products:
* **CVE-2026-16812** – **VeloCloudOrchestrator**
* **CVE-2026-20127** – **Cisco Catalyst SD-WAN**
* **CVE-2025-8875** and **CVE-2025-8876** – **N-able N-central**
* **CVE-2024-39717** – **Versa Director**
* **Quest KACE** (suspected zero-day)
Compromising these platforms grants threat actors extensive administrative control, enabling credential harvesting, remote access, and the ability to reach downstream customers without the 'noisy' lateral movement that might trigger detection systems.
*Source: Black Lotus Labs*
**Black Lotus Labs** elaborates in their report: “To construct these sessions, its operators exploit exposed web interfaces on SOHO, IoT, and other relay devices, then deploy only the tooling needed to enable chained SSH access through the compromised node. This included temporary SSH services, keys, configuration files, and “live off the land” utilities.”
Crucially, after each session, typically lasting less than eight hours, the threat actors meticulously remove all their tooling, keys, and configuration files from the disposable relays. By early 2025, the framework evolved to a hybrid model, incorporating both disposable relays and compromised enterprise systems retained for one to three months.
**Black Lotus Labs** believes 'Silent Train' is reserved for high-value targets and carefully executed, hands-on operations, often conducted within the China Standard Time (CST) timezone. The consistent use of zero-days against these targets further reinforces this assessment.
### Recommendations for Defense
To counter such sophisticated threats, security professionals are advised to:
* Strengthen security measures around centralized management systems.
* Restrict internet access to administrative interfaces.
* Prioritize rapid patching of all identified vulnerabilities.
* Centralize logs with extended retention periods for thorough analysis.
* Monitor for unusual administrative activity.
* Regularly review trusted connections that could expose customer or partner networks.
* Adhere to guidance from **CISA** and **NCSC** regarding **Volt Typhoon** activities.